 Defender
Google SecOps Out-of-the-Box SecOps Integration
Centralize threat telemetry and streamline SOC triage with Lumu’s native Google SecOps Out-of-the-Box Integration. Effortlessly stream real-time Lumu incidents and operational events into Google SecOps (formerly Chronicle), empowering analysts to perform fast retrospective threat hunting and accelerate threat mitigation.
 Defender
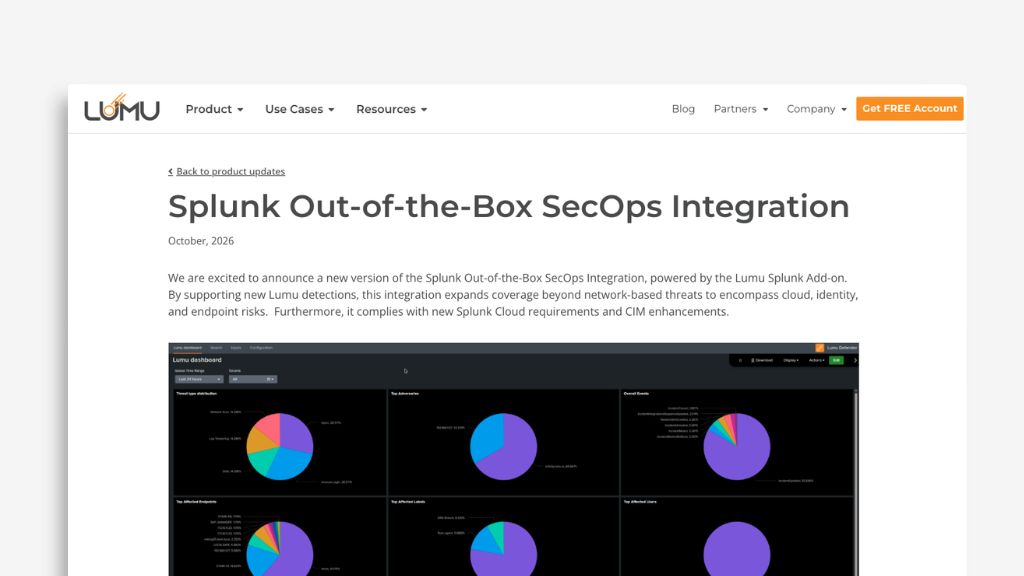
Splunk Out-of-the-Box SecOps Integration
Unify your threat event management across network, cloud, identity, and endpoint risks with the upgraded Splunk Out-of-the-Box SecOps Integration. Powered by the Lumu Splunk Add-on, this update delivers automated event syncing, standardized CIM mapping, and full compliance with Splunk Cloud requirements.
 Discover
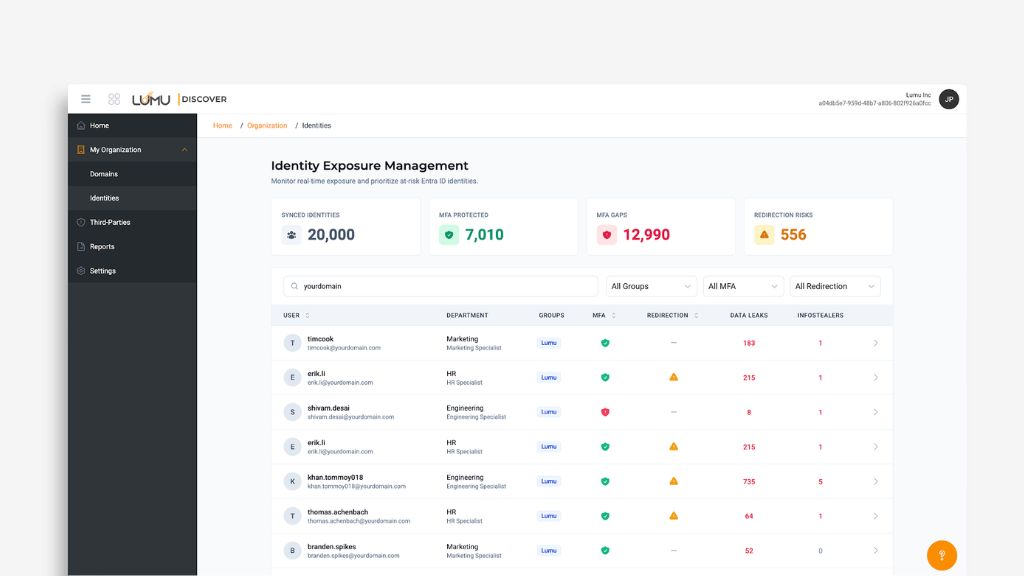
Identities View: Identity Security Posture Management (ISPM) Capabilities
Shrink your identity attack surface with ISPM capabilities in Lumu Discover. Powered by Microsoft Entra ID integration, the new Identities view correlates internal directory posture—like MFA coverage and email forwarding—with external data leaks and infostealer infections to pinpoint high-risk credential gaps instantly.
 Defender
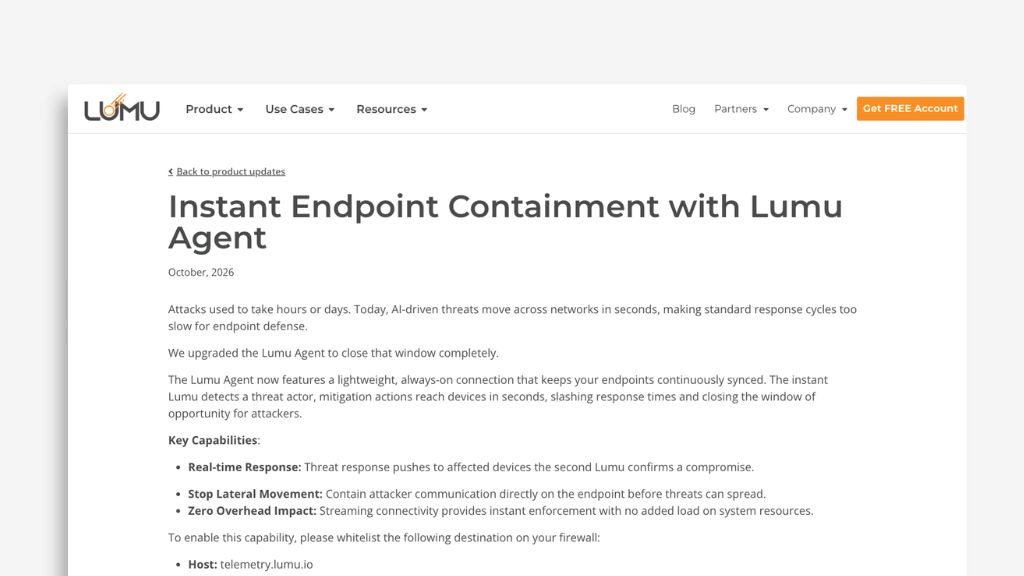
Instant Endpoint Containment with Lumu Agent
Modern AI-driven threats execute in seconds, making traditional response times obsolete. The upgraded Lumu Agent delivers Instant Endpoint Containment through a lightweight, always-on connection—pushing real-time mitigation to affected devices instantly to halt lateral movement before attacks can spread.
 Discover
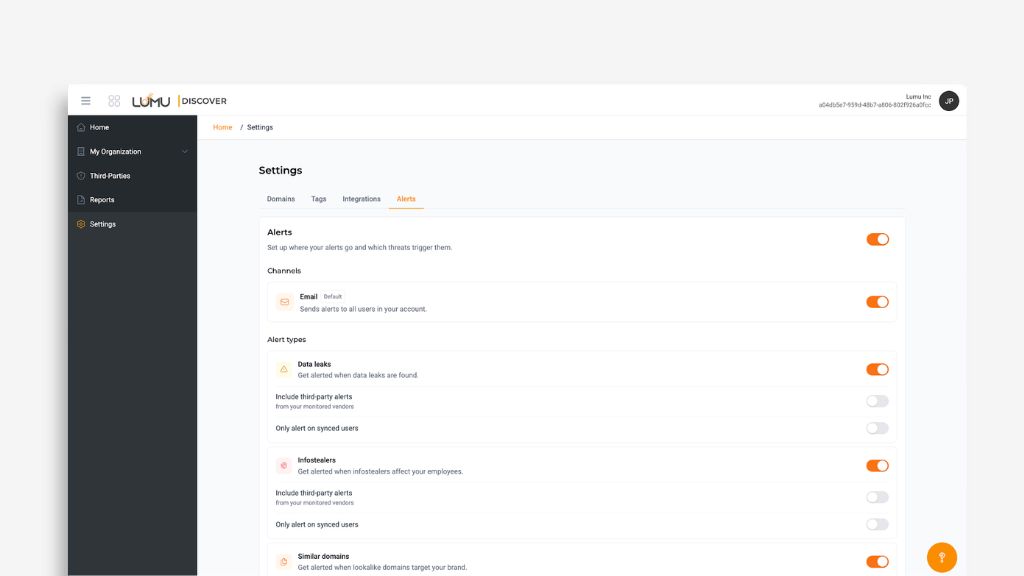
Customizable Email Alerts
Eliminate alert noise and focus on critical threats with Customizable Email Alerts in Lumu Discover. Easily tailor your email notifications by specific threat types, extend coverage to third-party vendors, and limit breach alerts strictly to active employees synced from your identity provider.
 Defender
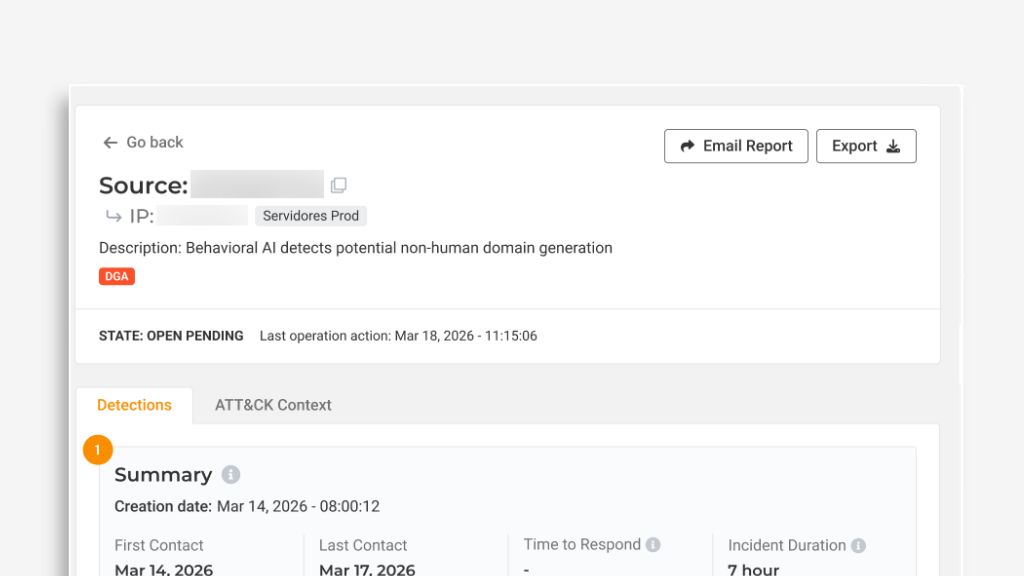
DGA Detection Incidents
Malware uses Domain Generation Algorithms (DGA) to hide Command and Control traffic. Lumu’s new DGA Detection Incidents update shifts DGA tracking from passive anomalies into active, prioritized SecOps incidents—allowing your team to instantly identify, isolate, and contain compromised assets.
 Maltiverse
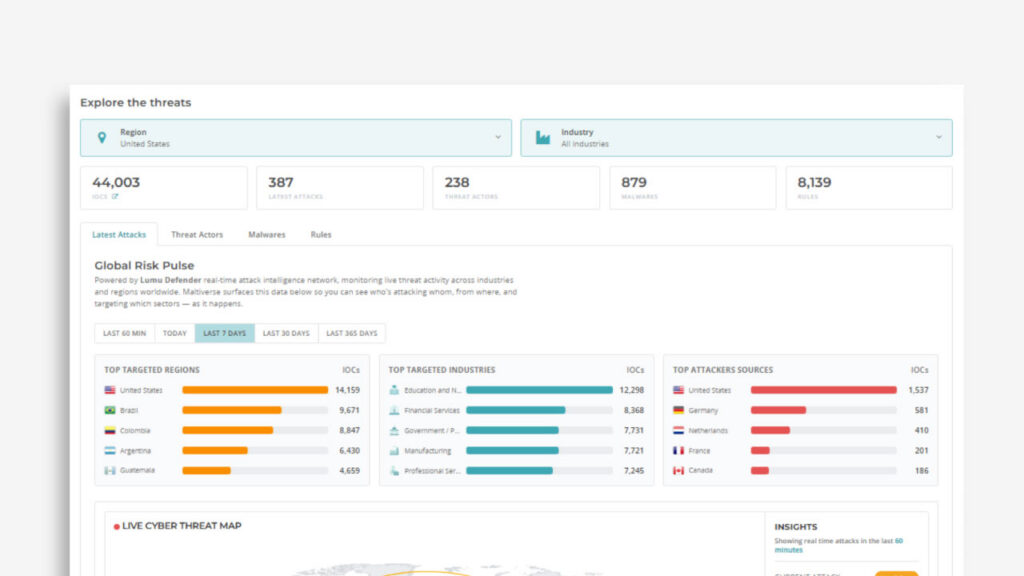
Lumu Threat Observatory™
Upgrade your threat detection pipeline with the Lumu Threat Observatory in Lumu Maltiverse. See live adversaries targeting your peers, build customized feeds, and push daily-updated YARA and Sigma rules straight to your Firewall, SIEM, or EDR in seconds.
 Defender
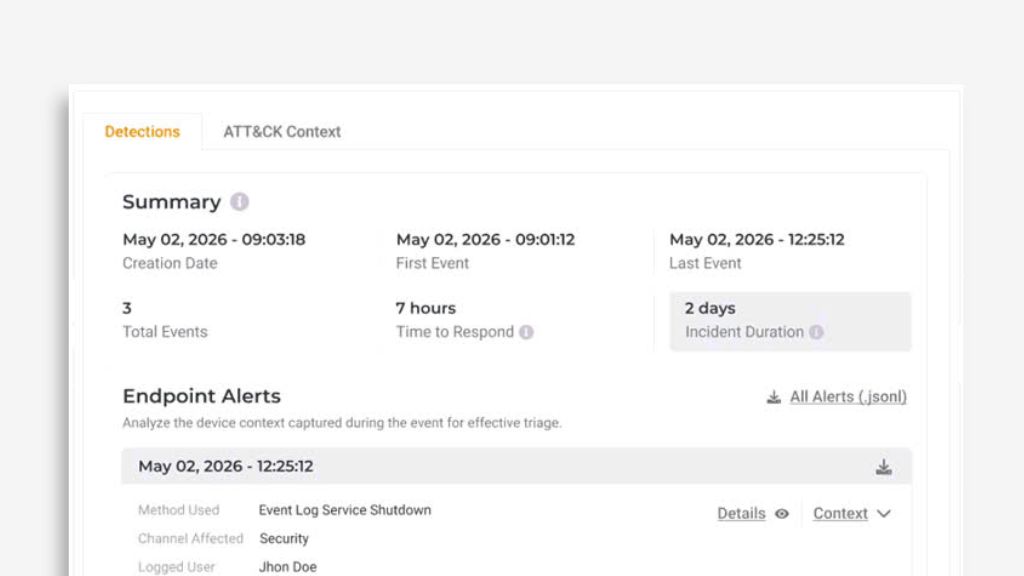
Log Tampering Detections
Before launching major attacks like ransomware, adversaries often clear or disable system logs to hide their trail. Lumu’s new Log Tampering Detections eliminate this critical blind spot, giving your SOC the real-time visibility needed to stop threats before encryption begins.
 Defender
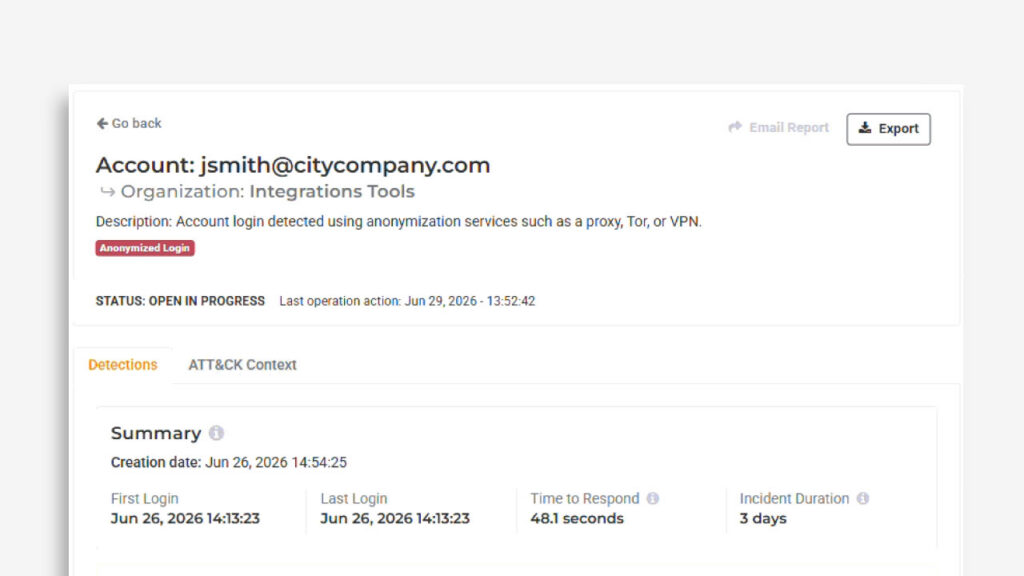
Anonymized Login Incidents
Threat actors are shifting from forcing entry to logging in with stolen credentials. Protect your network with ‘Anonymized Login Incidents’ in the Lumu Portal. Powered by Microsoft Entra ID, this feature detects anonymous logins (VPNs, TOR) and stops lateral movement instantly.
 Autopilot
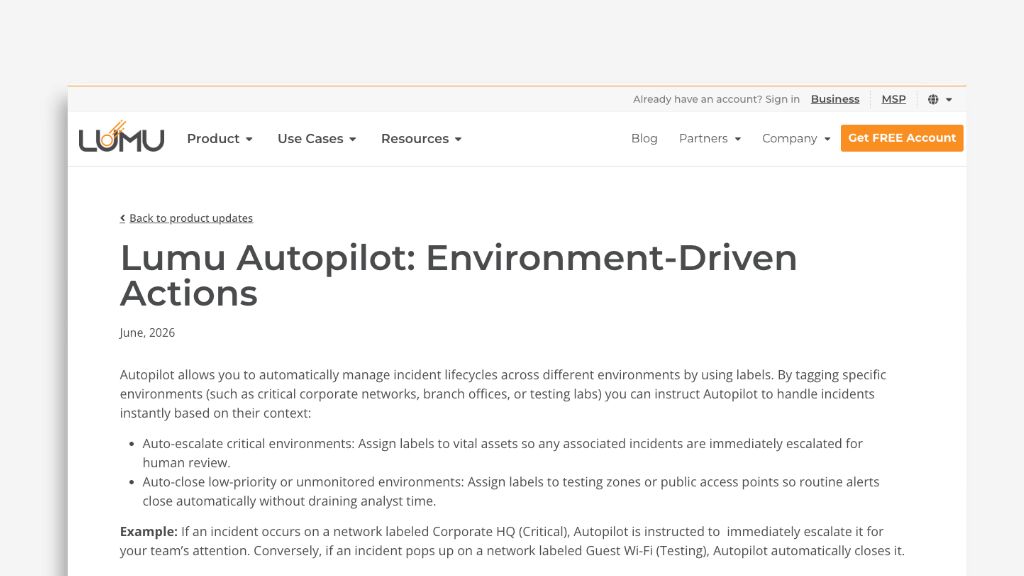
Lumu Autopilot: Environment-Driven Actions
Tailor automated threat response to your network architecture with Lumu Autopilot Environment-Driven Actions. By applying label-based policies across environments—like Corporate HQ or Guest Wi-Fi—Autopilot automatically escalates high-risk incidents for analyst review while auto-closing routine alerts to slash MTTR.
 Defender
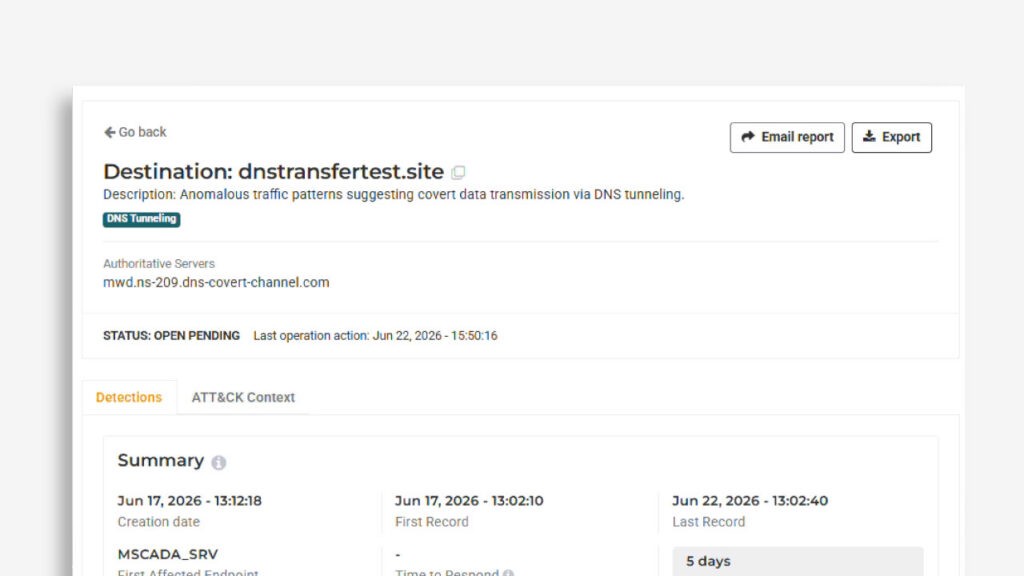
DNS Tunneling Incidents
Attackers are constantly searching for ways to blend into your day-to-day network traffic. One of their favorite hiding places is the Domain Name System (DNS). Because DNS is essential for standard internet operations, it is rarely blocked, making it a primary vehicle for cybercriminals looking to fly under the radar.
 Maltiverse
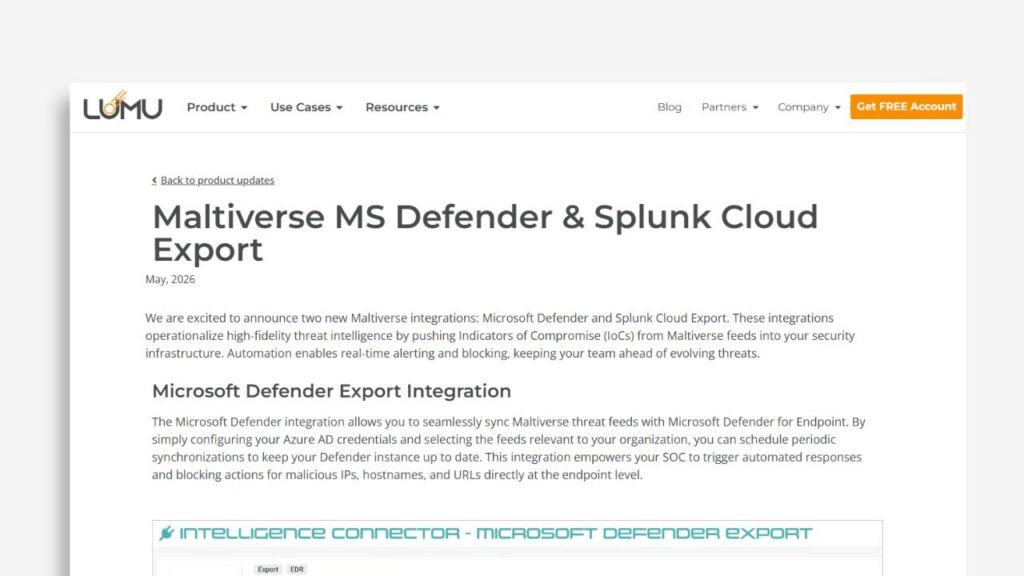
 MS Defender & Splunk Cloud Export
Learn how Maltiverse integrates with Microsoft Defender for Endpoint and Splunk Cloud to operationalize threat intelligence through automated IoC ingestion. This update enables security teams to trigger real-time blocking actions, enrich events, and maintain high-confidence detection workflows without manual data handling or complex integrations.
 Discover
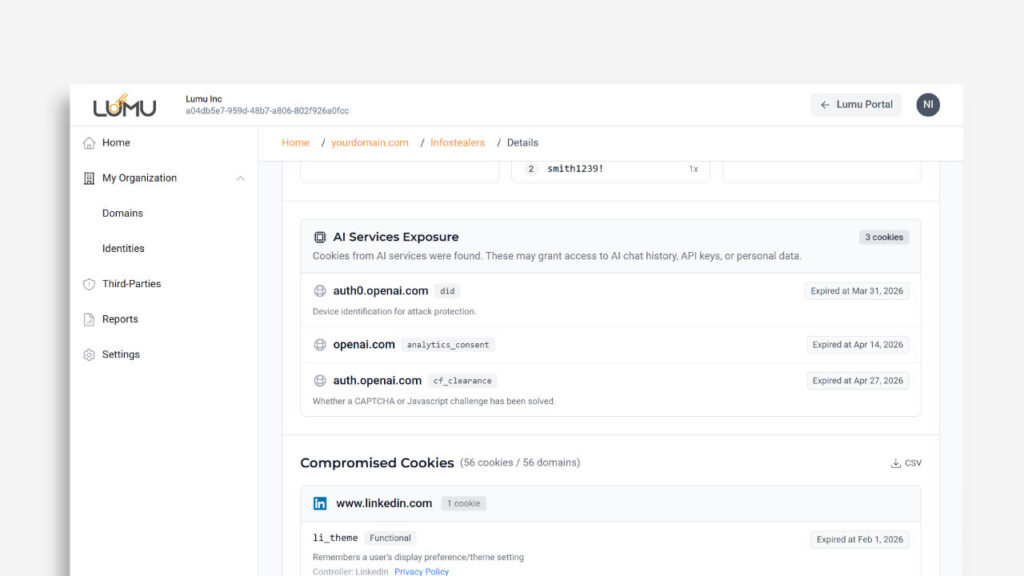
AI Services Exposure
While password theft is a major threat, modern attackers rely heavily on session cookies and system-level persistence to bypass security controls. We’ve enhanced Lumu Discover to give you full visibility into Infostealers-related incidents, with one of the biggest additions being the AI Services Exposure section.
 Discover
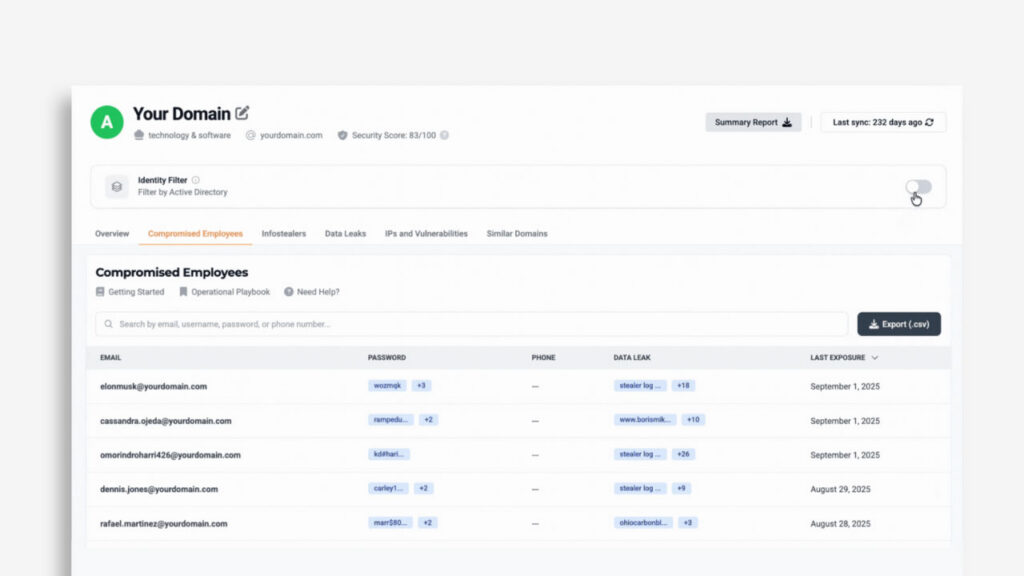
Lumu Discover: Active-Employee Threat Filtering
Eliminate dark web noise by correlating external leaks with your active employees to identify critical security gaps like disabled MFA or unauthorized email forwarding.
 Defender
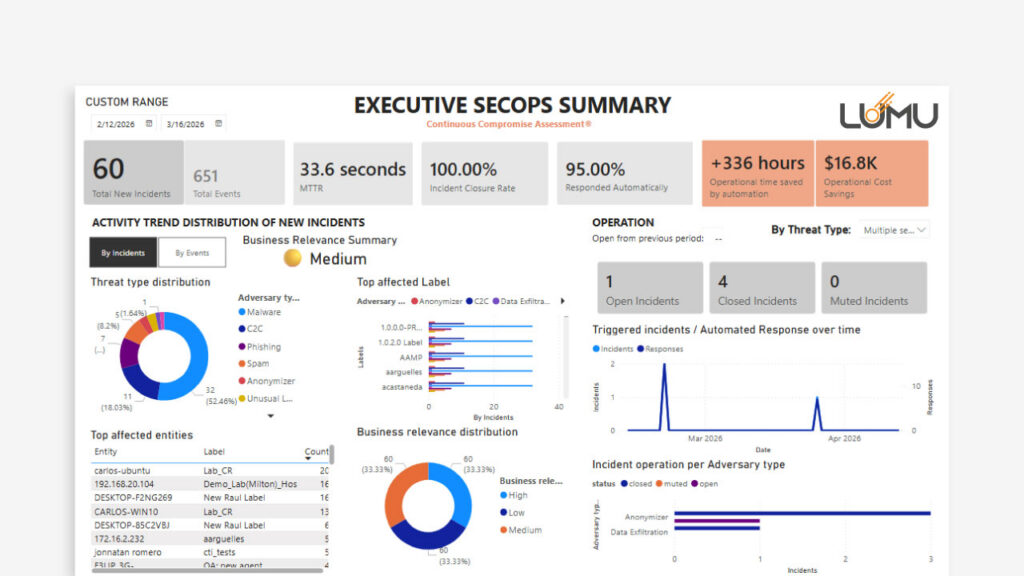
Lumu Defender Integration with Power BI
Learn how to integrate Lumu Defender with Microsoft Power BI to create executive-ready cybersecurity dashboards. This guide explains how to transform threat intelligence data into actionable insights, track key metrics like MTTR and incident closure rates, and demonstrate operational ROI using a ready-to-use template—without complex API scripting or manual data exports.
 Autopilot
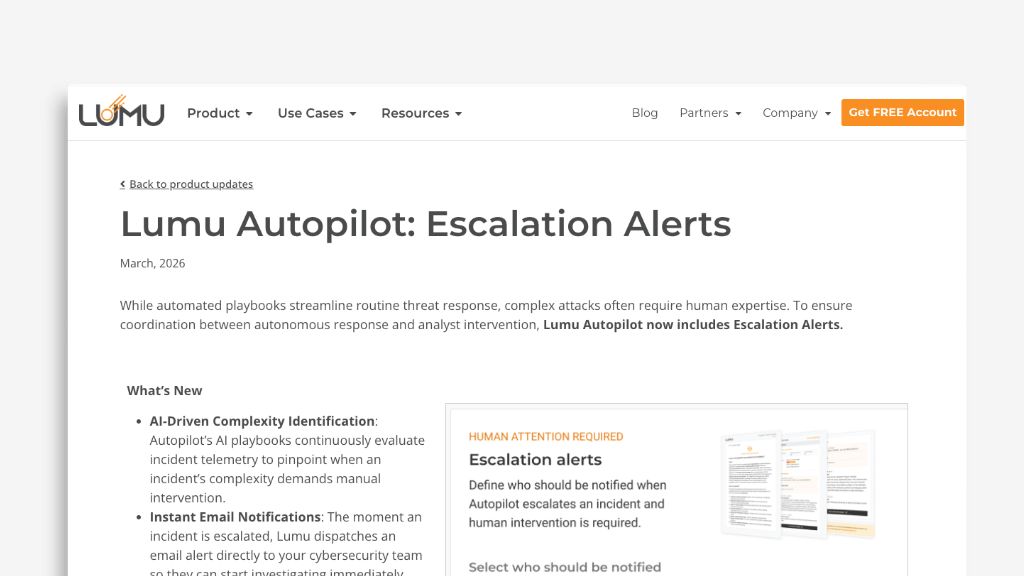
Lumu Autopilot: Escalation Alerts
Bridge the gap between autonomous response and human expertise with Lumu Autopilot Escalation Alerts. Autopilot’s AI playbooks evaluate incident complexity in real time, dispatching instant email alerts to your analysts when manual intervention is required for high-priority threats.
 Defender
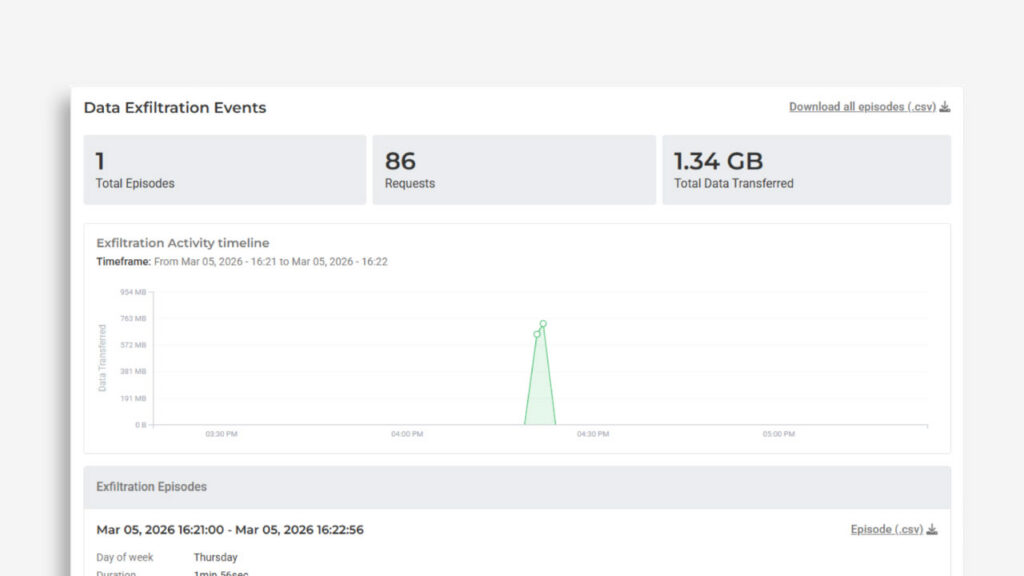
Data Exfiltration Incidents
Ransomware groups have shifted to double extortion, often stealing sensitive data before a single file is ever encrypted.
Most modern attacks are “Living off the Land,” using legitimate tools like Rclone or Mega to move data. These connections often bypass traditional security rules because they look like normal cloud traffic.
 Defender
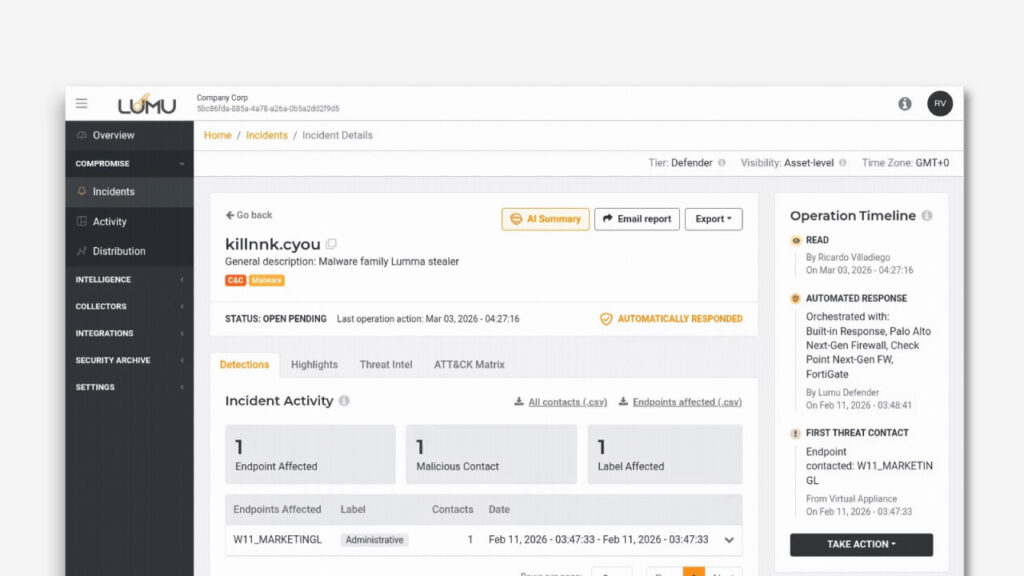
Lumu AI
We are excited to announce that we are making Lumu AI a standard feature, available to every Lumu Defender customer, not as a luxury add-on. Lumu AI instantly transforms complex network telemetry into high-fidelity, actionable intelligence to bridge the response gap and accelerate your Mean Time to Understand (MTTU).
 Defender
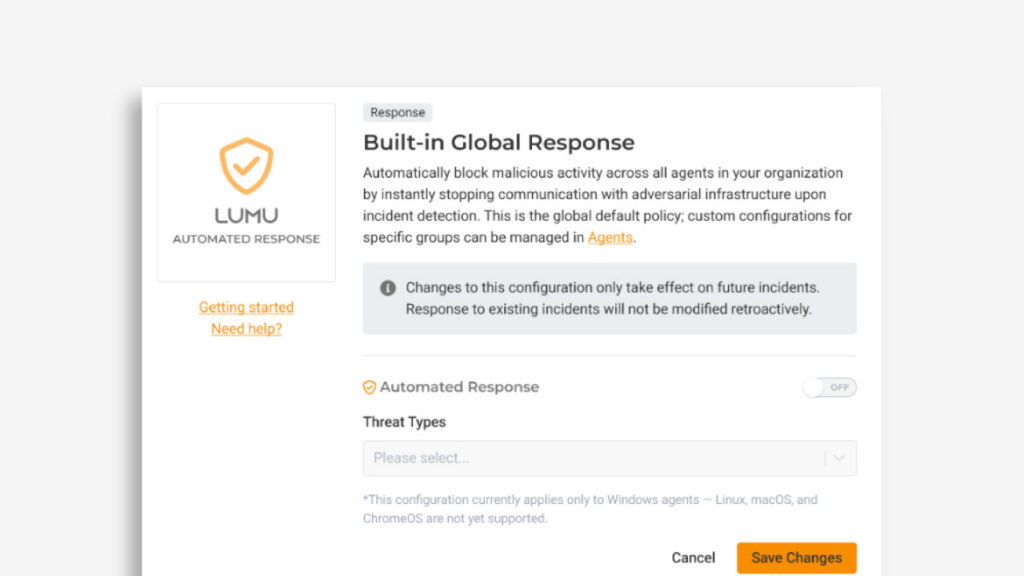
Lumu Agent with Built-in Response
The Lumu Agent now includes built-in automated response capabilities, expanding its role beyond data collection to enable direct action when threats are detected.
 Defender
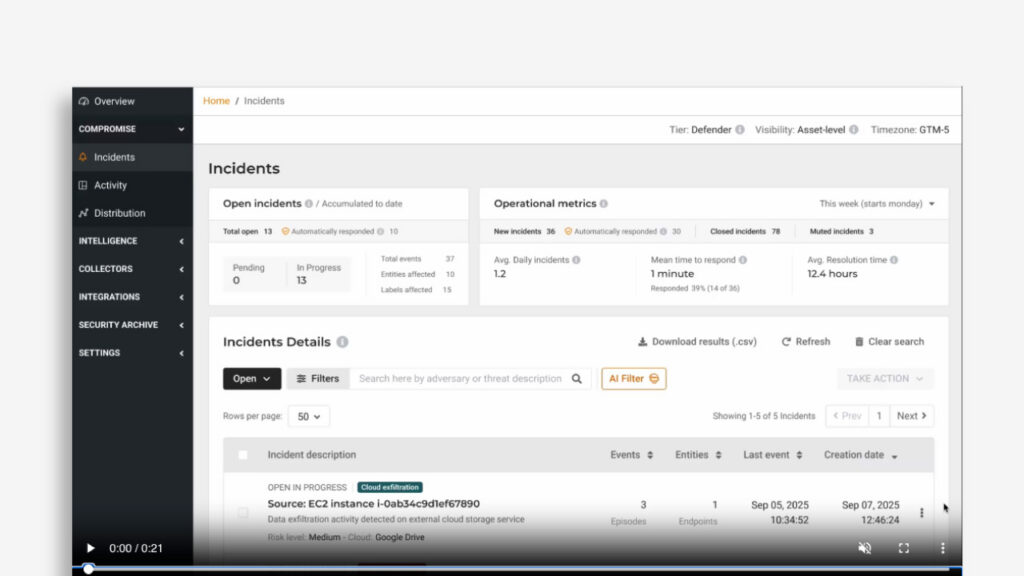
New Incidents Related to Anomalous User Behavior
Account takeover is one of the most common compromise paths, often achieved through phishing, info-stealers, or password reuse. Because attackers use valid credentials, they easily bypass traditional controls.
 Discover
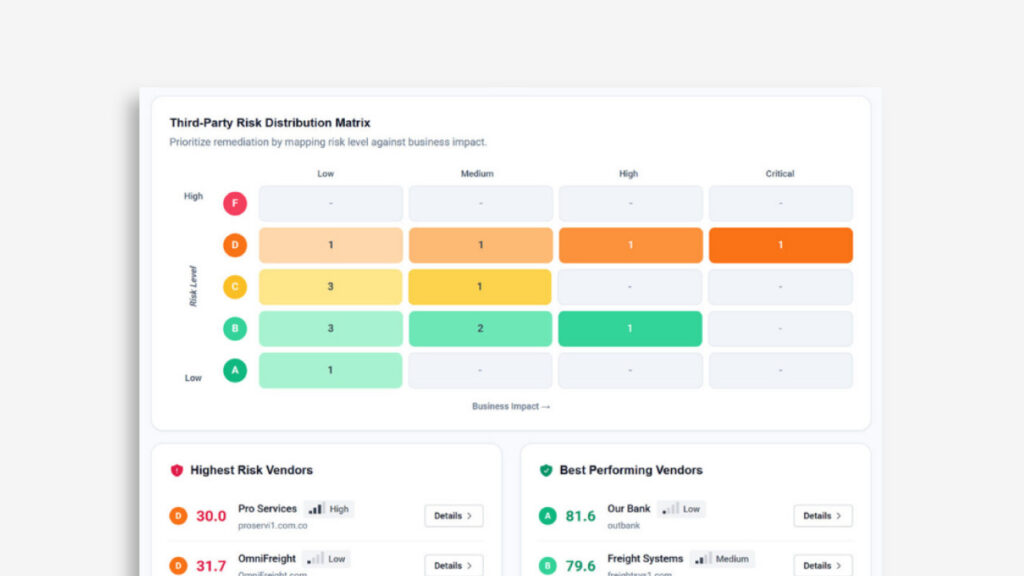
Lumu Discover: 3rd Party Ecosystem Risk
Lumu Discover now includes 3rd party risk assessment, giving you a complete picture of cybersecurity risks across your entire software ecosystem, including your technology vendors.
 Maltiverse
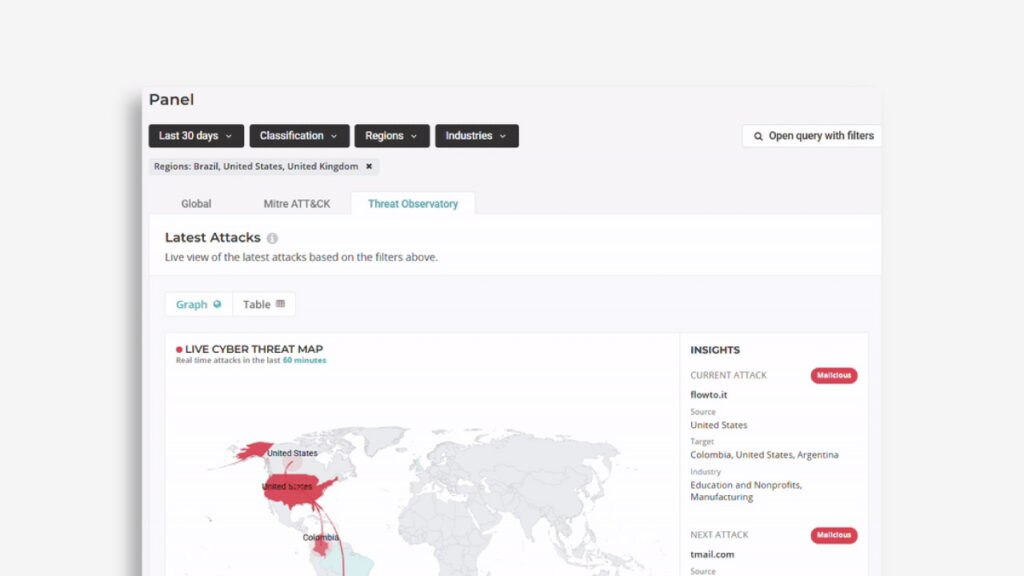
 Threat Observatory
When global cyber threats feel like constant noise, the real question isn’t just what the threat is, but whether it’s actually targeting your industry, region, or peers.
 Defender
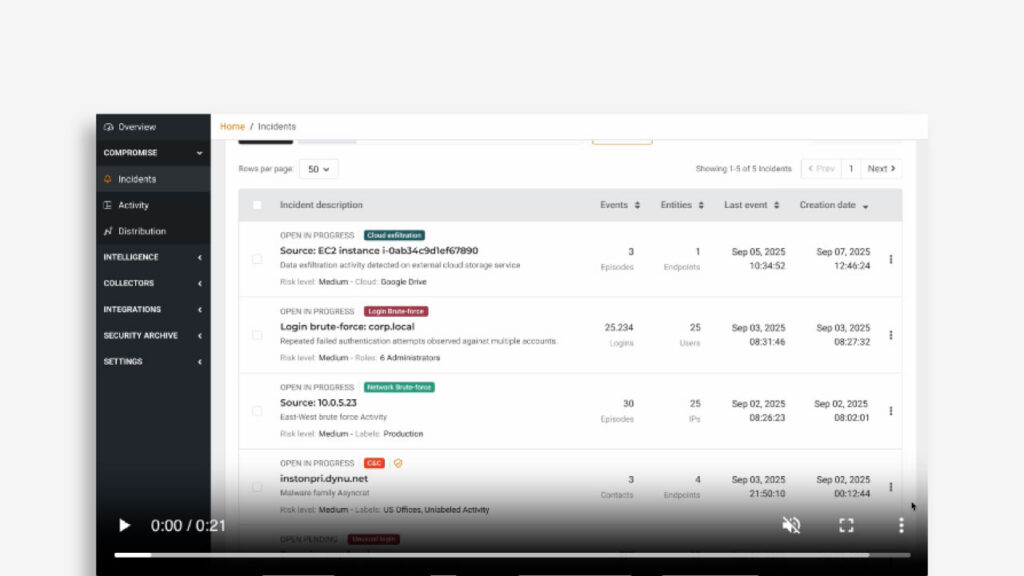
The Next Generation of Continuous Compromise Assessment®
Since its inception, Lumu has built Continuous Compromise Assessment as the foundation of how organizations detect and respond to threats, and it has served as the backbone of how thousands of security teams operate cybersecurity on a daily basis.
 General
Product Recap 2025
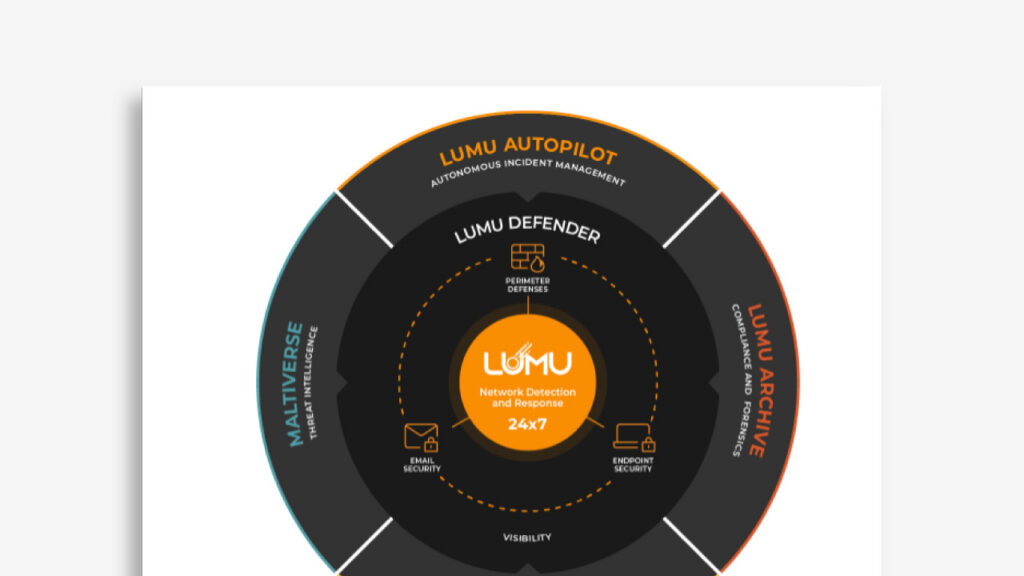
This year began with the launch of the Lumu SecOps Platform. Organizations no longer want vendor lock-in. They demand interoperability, open architectures, and the
 Defender
Lumu Portal Audit Logs
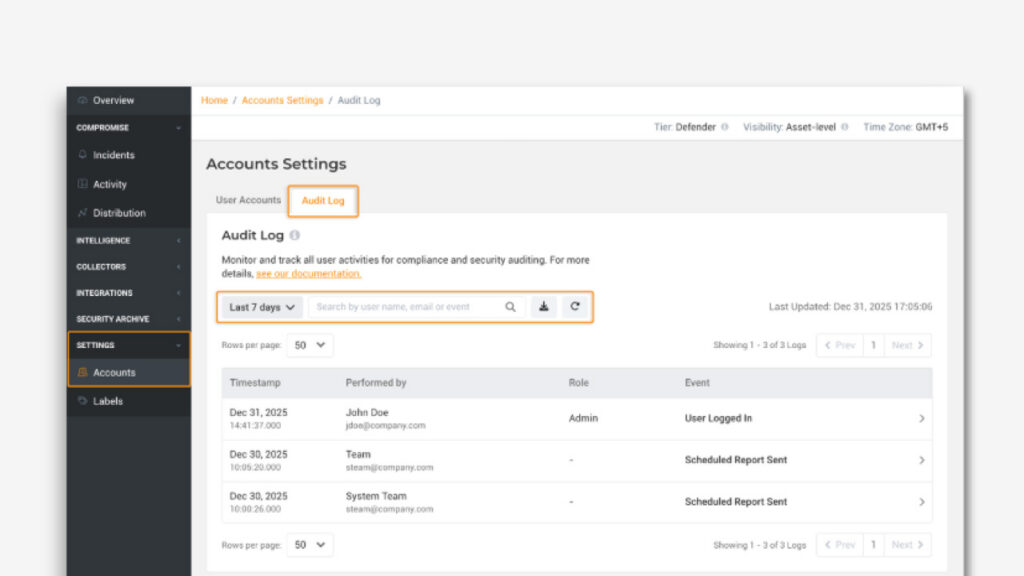
Audit Logs give your team a clear, auditable record of what’s happening inside the Lumu Portal.