
Table of Contents
On June 25 of this year, the Lumu Intelligence team published the results of an investigation into a payment fraud operation focused in the Latam region, specifically Colombia. The attacker replicated public services utility payment portals and other types of entities, positioned them in the search results of major search engines, and waited for the victim—trusting the search engine results—to reach these sites and make payments on the fraudulent portals. That report concluded with 51 domains, 4 IP addresses distributed across 4 autonomous systems, and seven months of partially reconstructed activity.
We picked up the trail of the operation again to delve deeper into a scheme that remains active, incorporating new brands and sectors relevant to the country’s economy. 288 domain indicators, 246 IPv4 addresses, and 29 identified autonomous systems—nearly six times more surface area than previously identified in the same operation.
This report presents the complete reconstruction of the operation and documents, for the first time, the threat actor behind it.
How the Attack Works
The entry point remains the same: the attacker prepares sites that impersonate the payment sections of legitimate services, positions them in major search engines, and waits for the victim to use these suggestions to pay their bills. What is unique this time is that we successfully identified the procedure used to position these sites before deploying the impersonated page. Essentially, the attacker configures informative sites about the page they intend to impersonate, containing the service’s rates, payment guides, and answers to common search queries. They leave these sites online for months to organically build search engine rankings. While the site only provides information, there is nothing to report and nothing for an antivirus to detect, allowing it to rise in search results without drawing attention.
The payment mechanism identified in the previous investigation, implemented on the Bre-B platform using QR codes, remains operational through three variants: two dedicated payment gateways and a third integrated directly into the replica’s domain. Furthermore, the associated Bre-B keys point to three independent collection accounts. All three codes are issued under the Redeban scheme, and each includes the merchant name and its category declared within the QR structure itself, indicating that behind each key is a merchant formally registered with the network. Two of these codes are static (they do not specify the amount, allowing the same key to collect any amount from any victim), while the third includes a predefined amount.
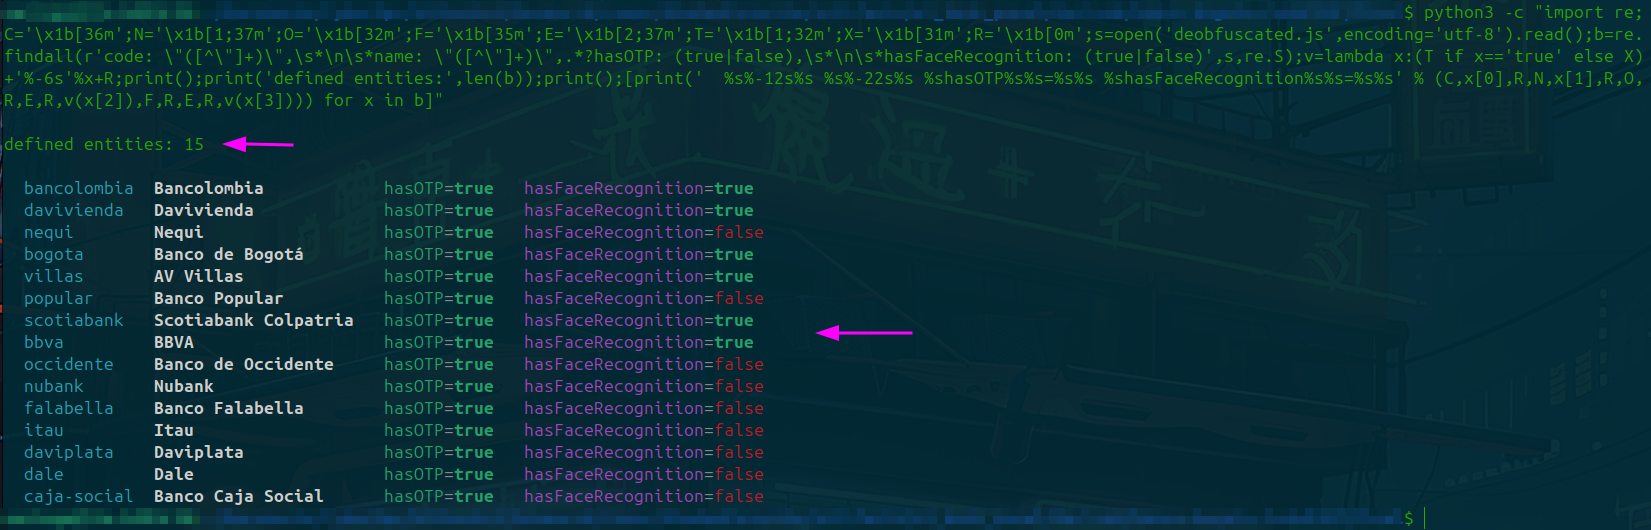
Behind some of these fake portals, the victim does not use any QR code to pay, but instead enters their online banking credentials into a replica of their financial institution’s portal. This panel impersonates fifteen Colombian financial institutions using a single codebase; additionally, it requests the six-digit verification code (dynamic token) received via app or SMS, debit or credit card details, and, in six of the fifteen entities, live facial biometric capture via photo and video.
The following is a real-world case from the financial sector as an example to understand the flow and impact of the campaign.
The Case of habi-pagar[.]st
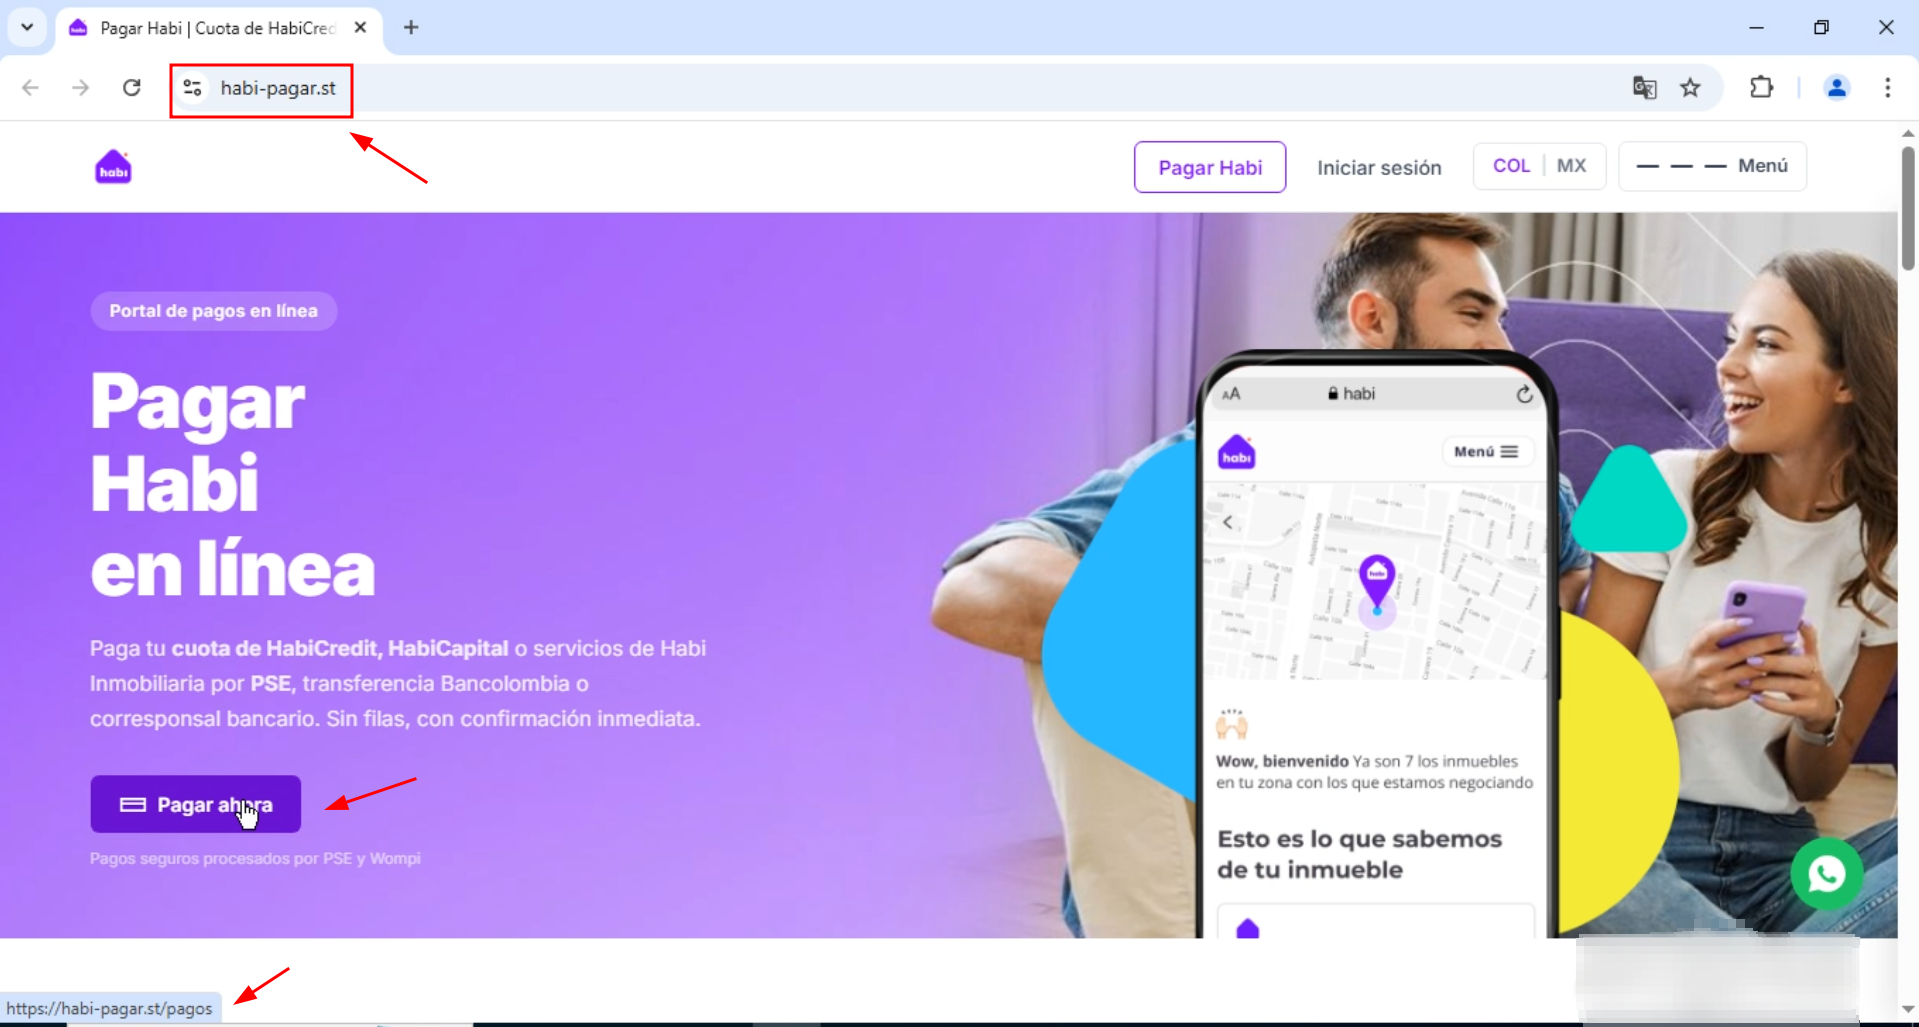
Habi is a Colombian real estate platform. The attacker registered habi-pagar[.]st on June 13, 2026, and configured a replica of its payment section there, including logos, payment gateway badges from the legitimate site, and a complete set of structured SEO tags to ensure search engines index it as if it were the official Habi site.
Impersonation Site
Upon entering the fraudulent payment portal, the victim observes an environment that, at first glance, exhibits no suspicious signs. However, once they click the “Pagar ahora” (Pay Now) button, the site redirects them to the path habi-pagar[.]st/pagos.
Information Gathering
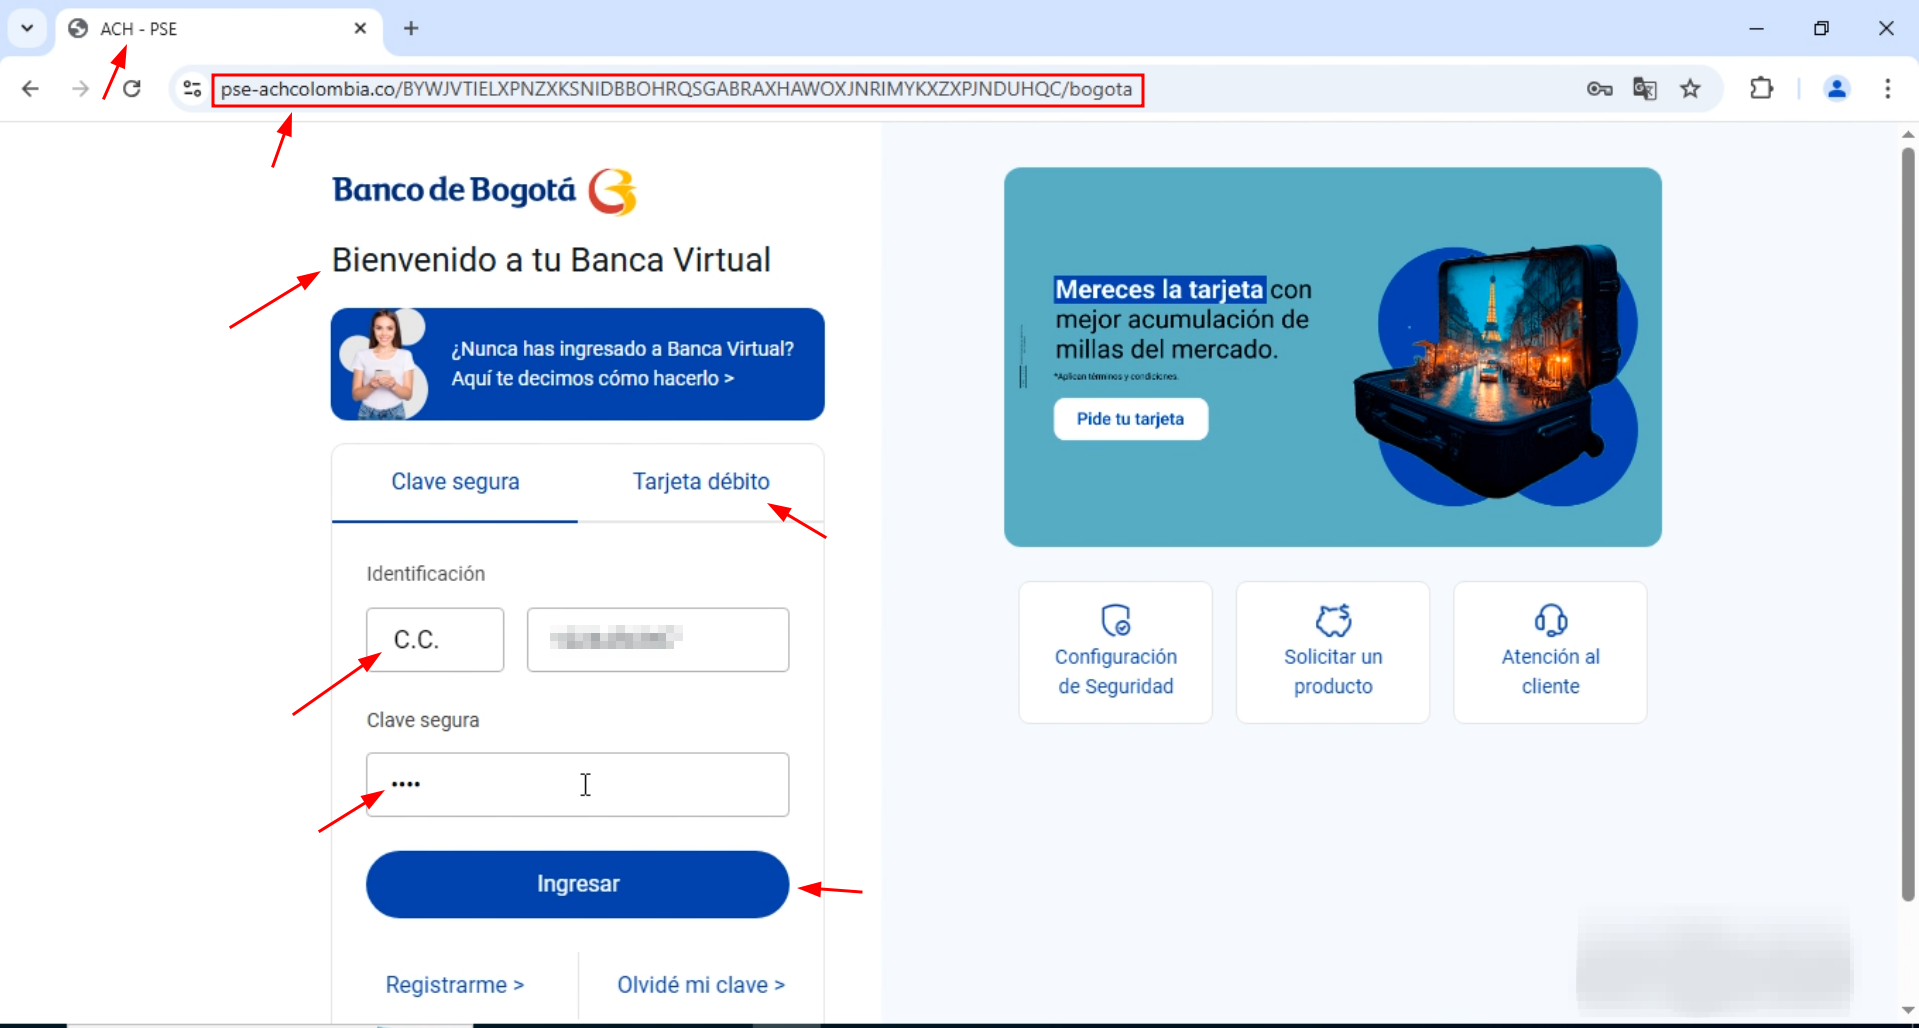
Once the redirection is complete, the victim is presented with a payment panel where they are prompted to enter the amount to pay and select their banking institution before clicking the “Continuar con tu pago” (Continue with your payment) button. Next, the site loads a form to collect basic information, which ultimately leads to the critical phase of this attack vector: the harvesting of banking credentials. At this point, the victim is redirected to the domain pse-achcolombia[.]co, where they are asked to provide their identification number and online banking password.
After waiting a few seconds while the server processes the response, the site displays a verification interface managed by the attacker. On this screen, the victim is asked, “for their security,” to check their banking app and enter a six-digit verification code (dynamic token).
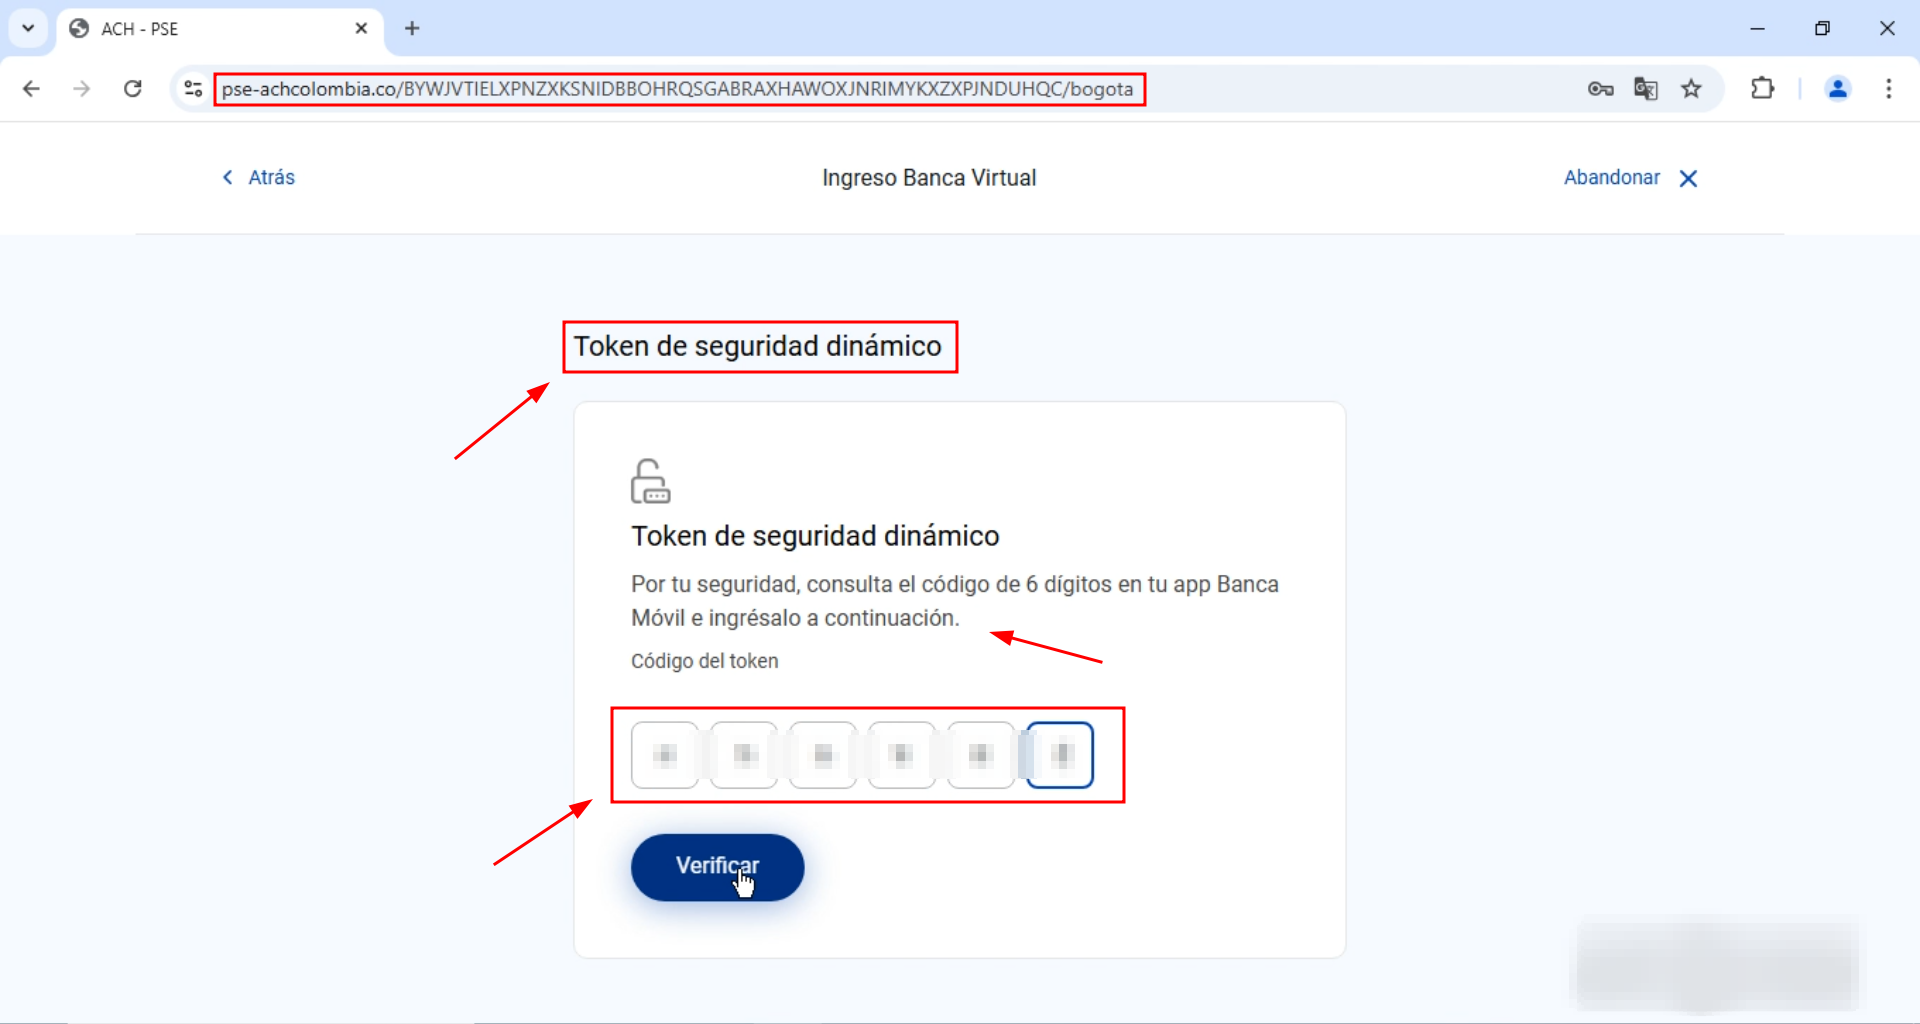
After another period of time, the page displays a message indicating to the victim that their details do not match, prompting them to verify and try again. At this stage, the threat actor has already harvested the victim’s banking credentials and dynamic security token; the latter highlights that the attacker must operate quickly before the dynamic code expires or changes.
Adversary Infrastructure
The operation is sustained by bulletproof or abuse-tolerant hosting providers historically used to facilitate such activities; it is on this infrastructure that the attacker configures their replicas and keeps them active. The domains rotate in batches from one server to another, meaning the same group of names reappears together on the next provider. In most cases, it is not possible to determine where they are hosted, as the attacker places them behind a protection service from the moment of registration.
Nodes Topology
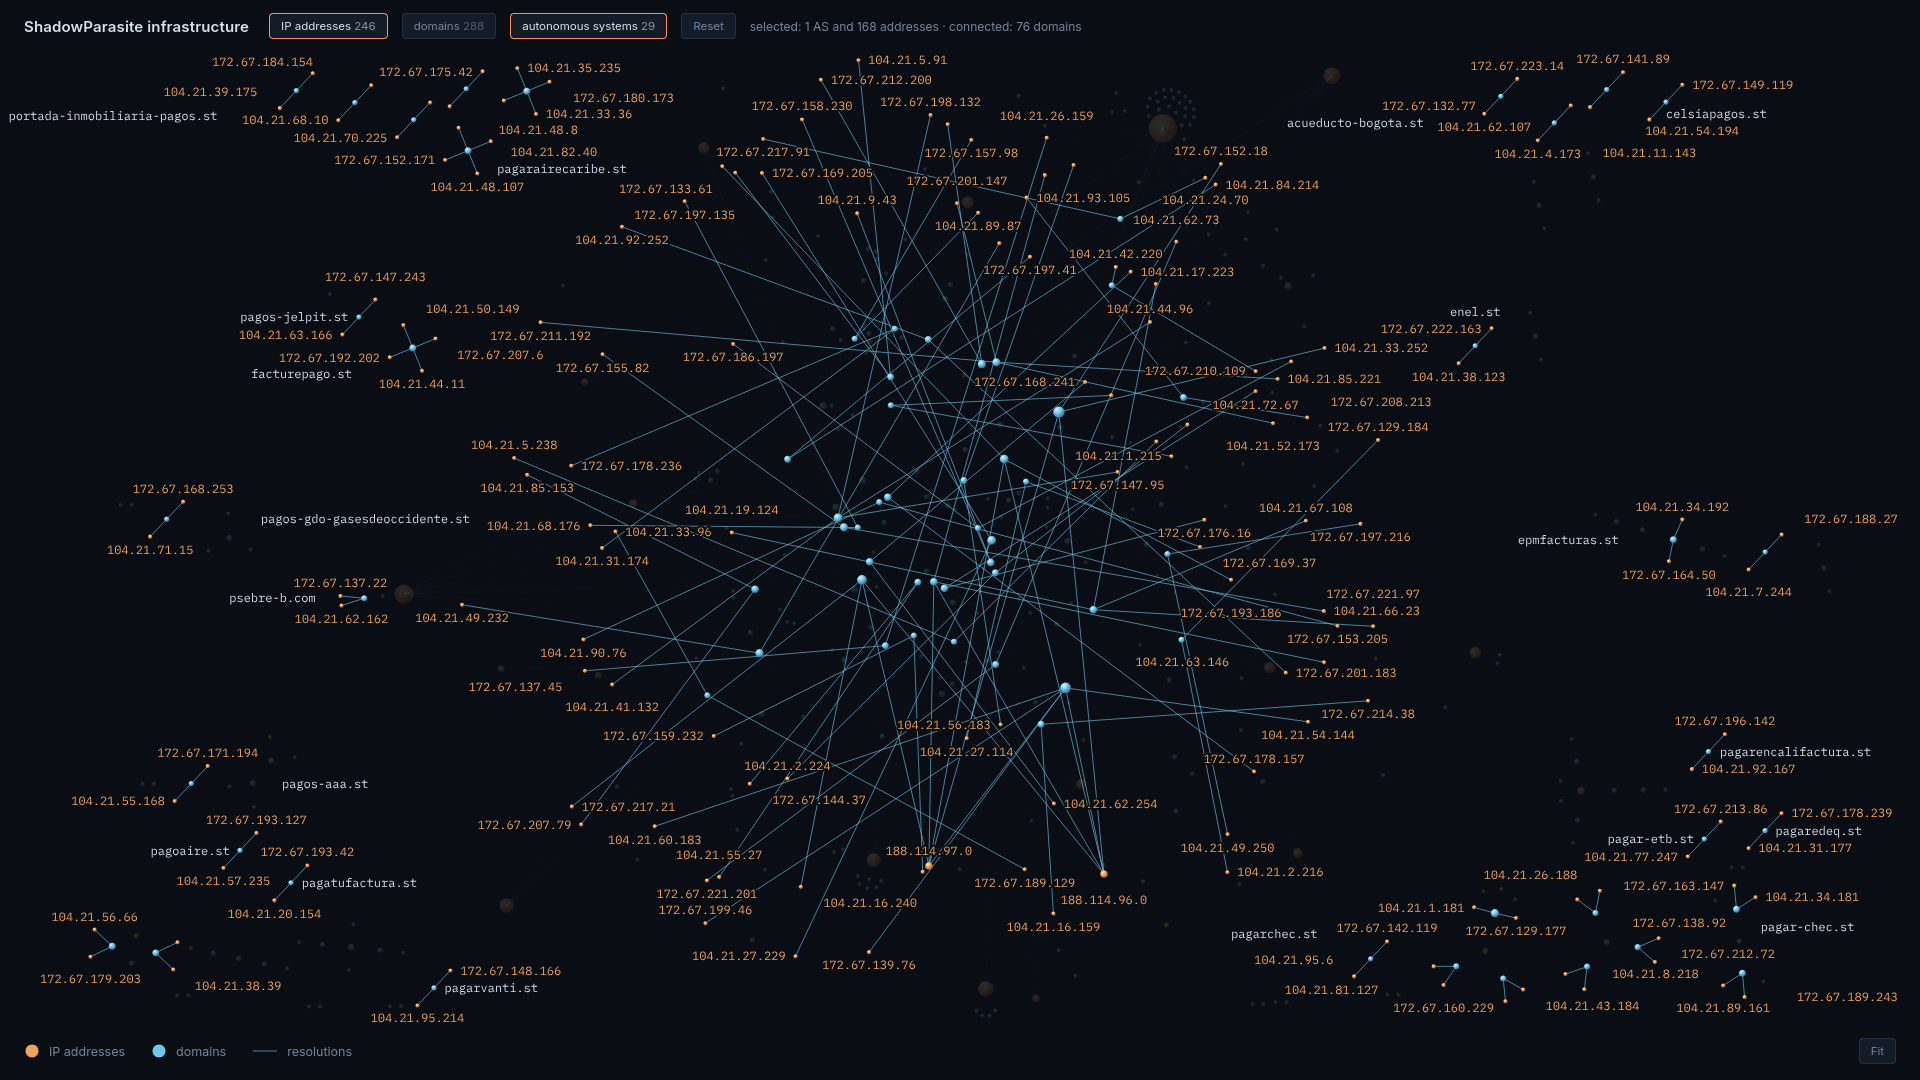
This investigation identified 246 IPs, 288 domains, and 29 autonomous systems, which are represented in the following constellation, where orange nodes represent IPv4 addresses, blue nodes represent domains, and the connections represent observed resolutions throughout the cybercriminal operation.
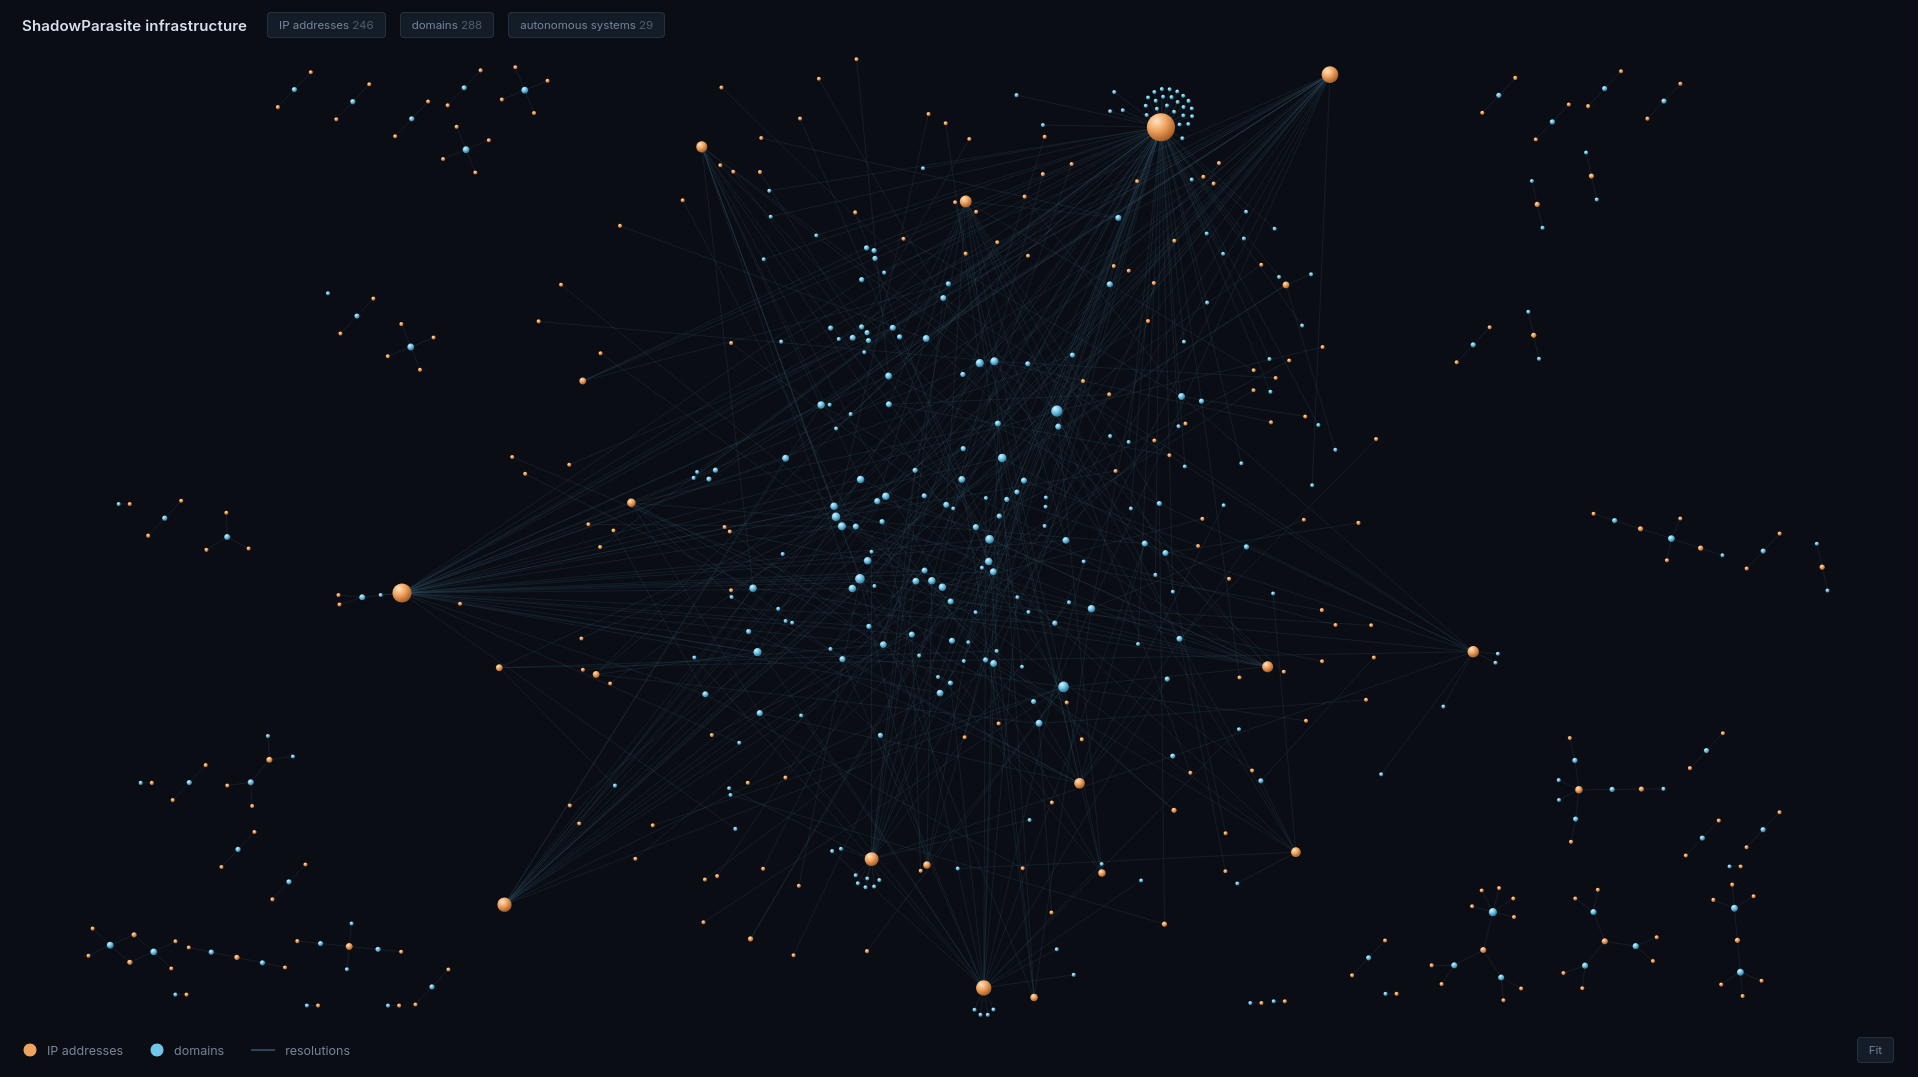
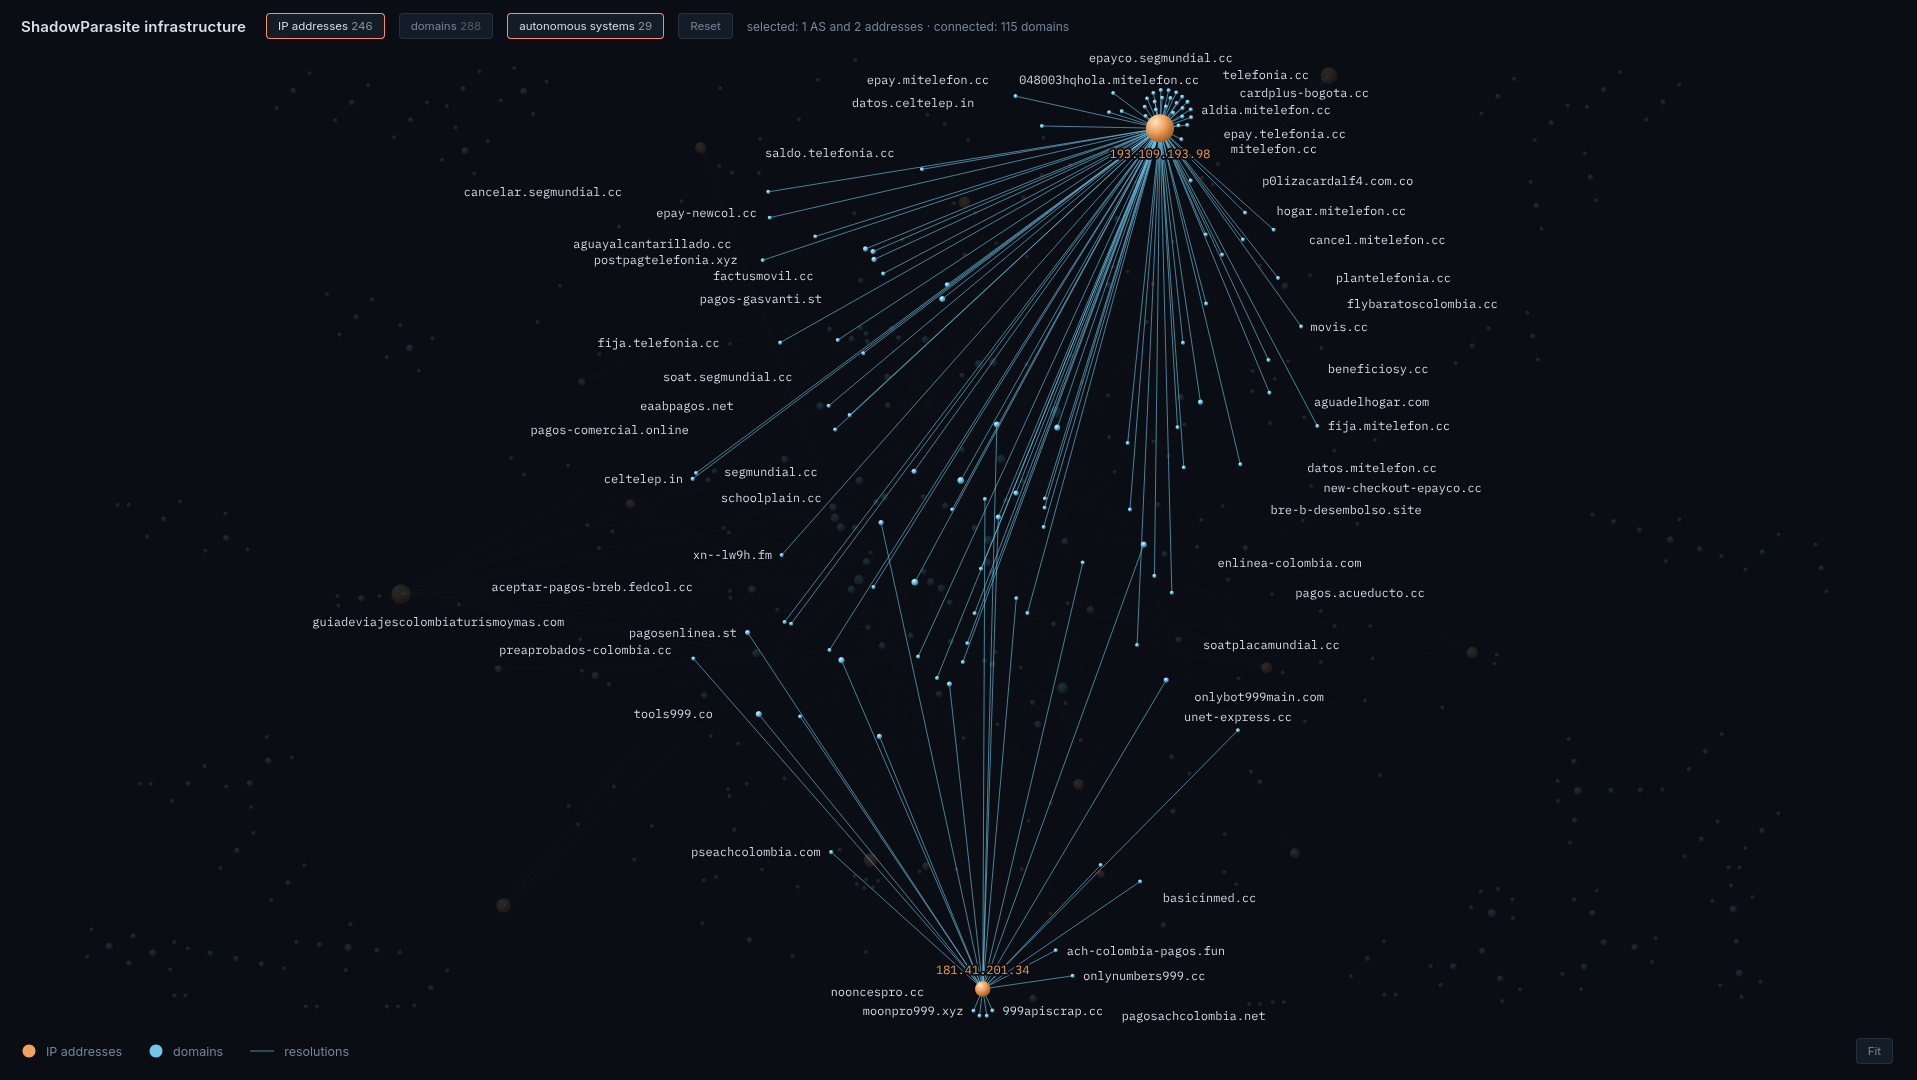
The IP address with the highest activity throughout the operation is 193.109.193[.]98, belonging to Datacamp Limited AS212238, where the attacker operated 91 domains between January 14 and June 24, 2026. This infrastructure does not appear to be shared hosting; all 91 names observed resolving to it belong to the operation.
In the constellation, Datacamp Limited AS212238 has another active IP, 181.41.201[.]34 , which ranks fourth among the most active IPs, with 25 hosted domains observed. This single AS allowed the attacker to deploy 115 domains, representing 40% of the total identified infrastructure.
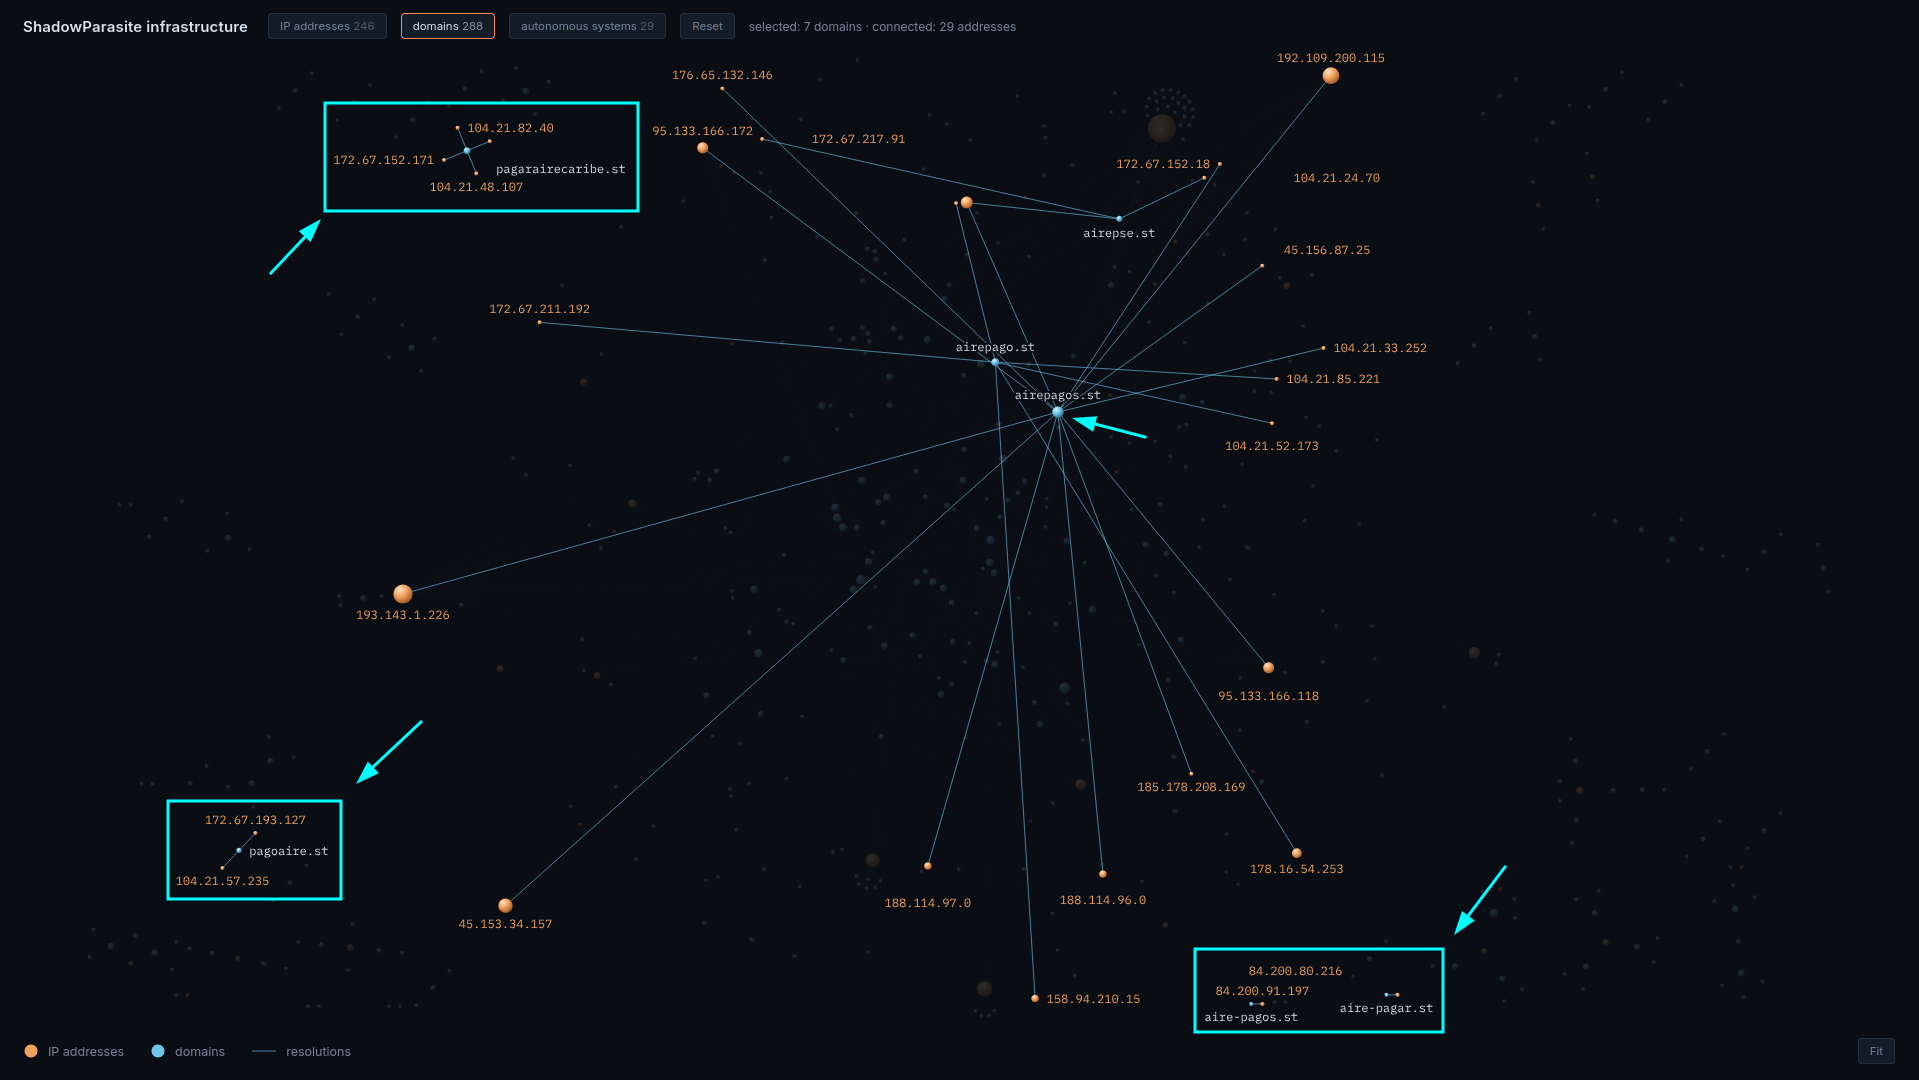
The domain with the highest activity is airepagos[.]st; in fact, the investigation was initiated following a detection of this domain in the LUMU system. Registered on December 8, 2025, the domain continues to resolve actively and load the fraudulent payment portal. During its more than 270 days of activity, it has migrated across 13 IP addresses distributed over 6 autonomous systems (AS).
As part of the topology analysis, filtering domains by the term “aire” revealed that the attacker has registered 6 permutations of “airepagos” throughout the operation. Of these, 4 are hosted on isolated satellite nodes away from the main core of activity.
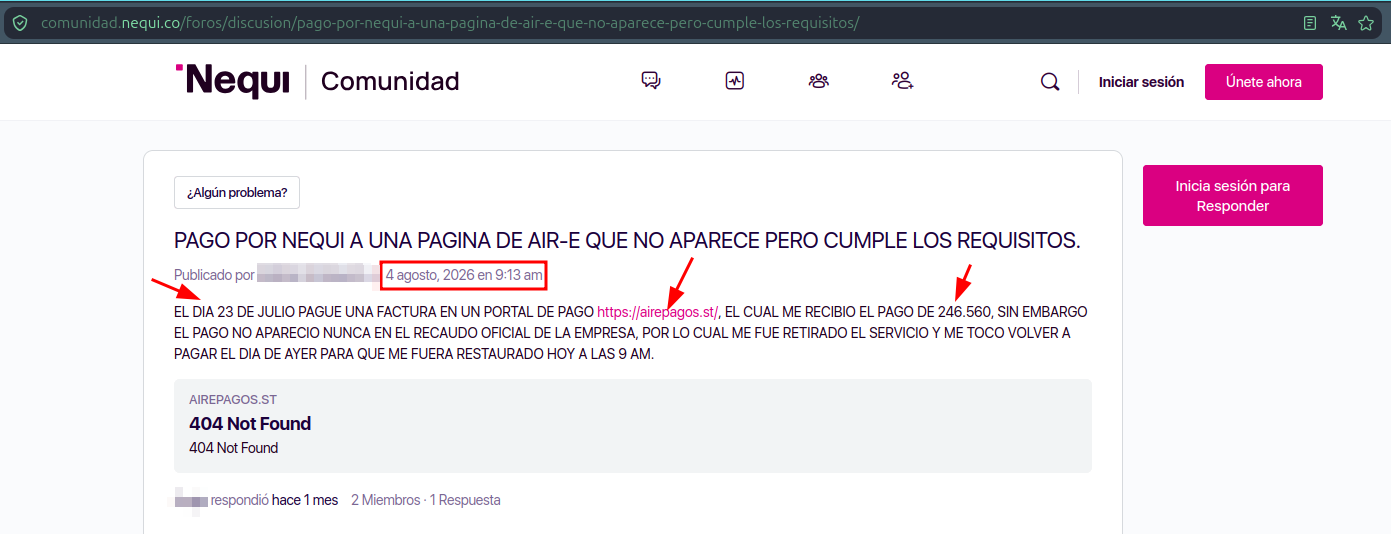
There are recent public reports associated with this domain where affected users recount their incidents; an example is the following thread from the Nequi community forum.
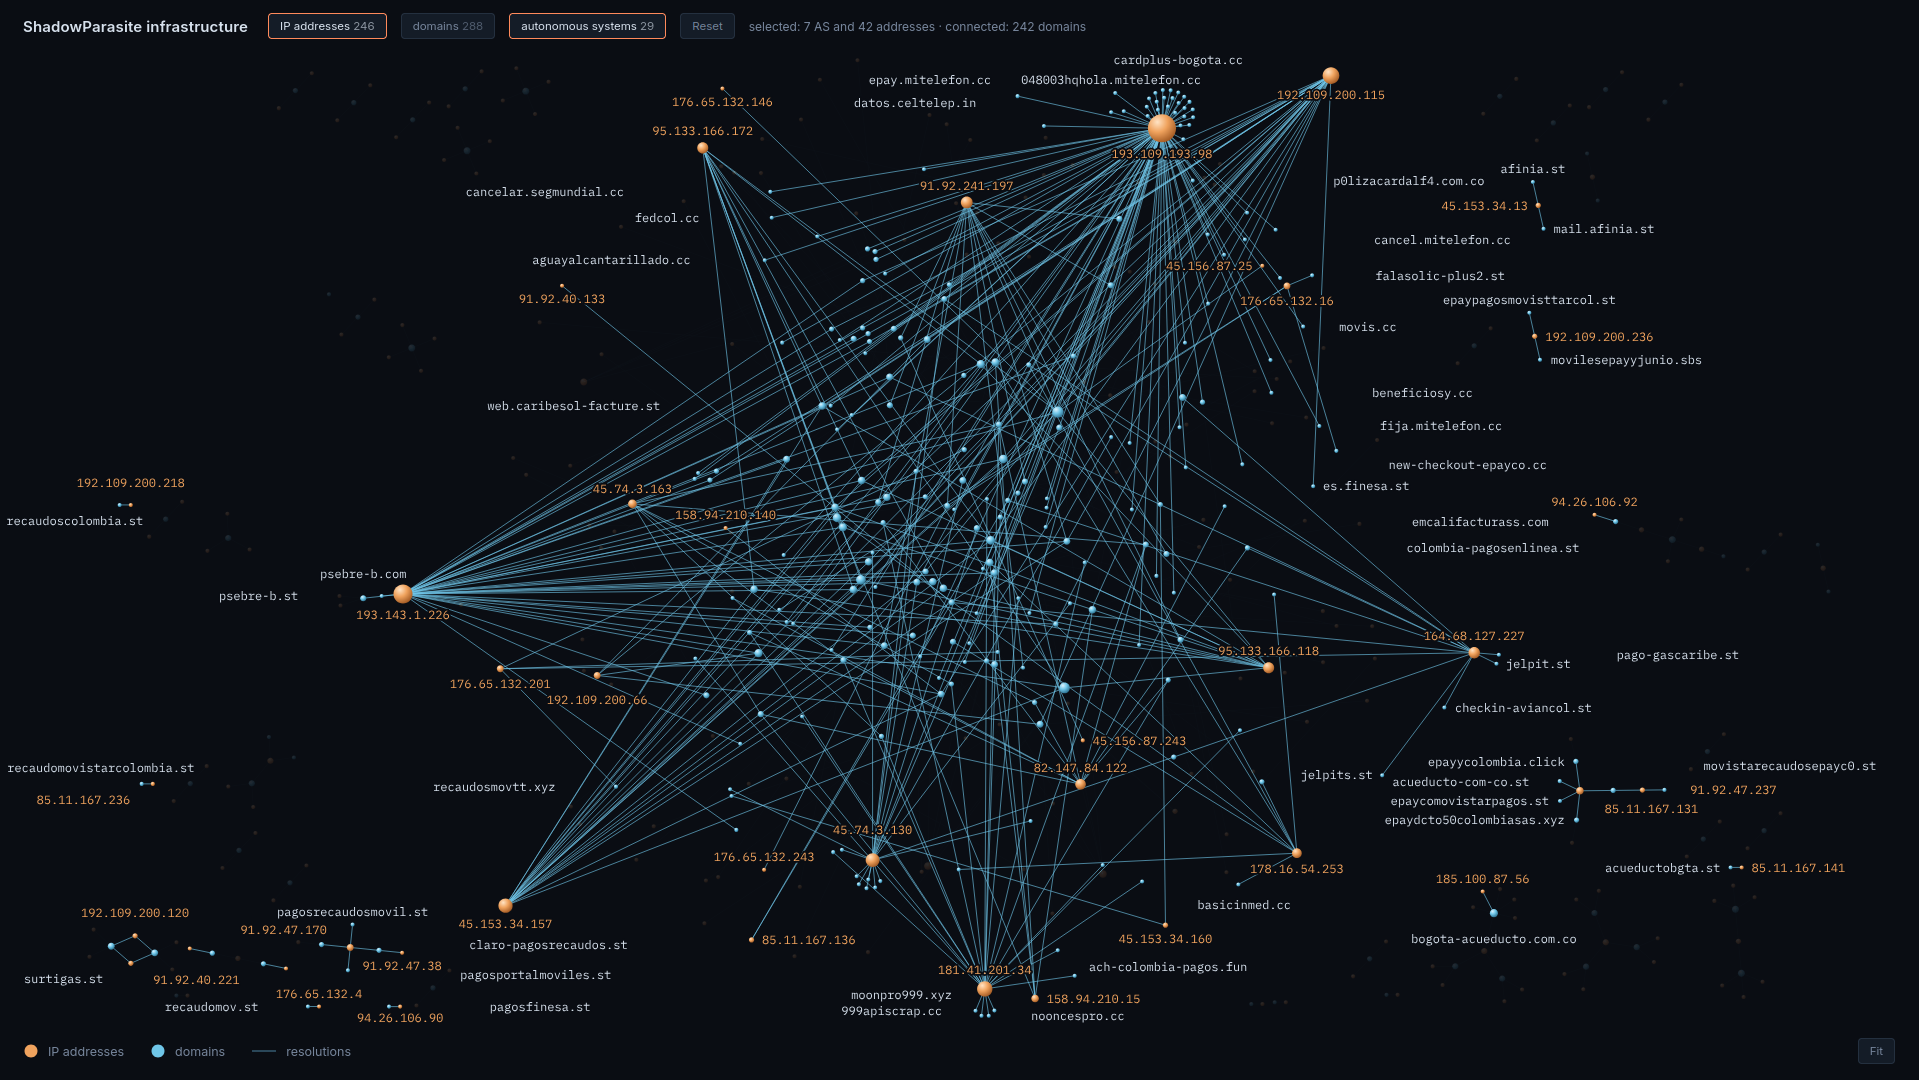
To date, the attacker has distributed their operation across 29 AS over ten months. However, 7 of them concentrate 242 of the 288 domains in the inventory—representing 84% of the total—consistently shifting the same group of domains among this set of providers.
| AS | Name | Domains | IPv4 |
| AS212238 | Datacamp Limited | 115 | 2 |
| AS197170 | TechTies Inc. | 74 | 28 |
| AS198953 | Proton66 OOO | 40 | 1 |
| AS211860 | Nerushenko Vyacheslav Nikolaevich | 33 | 3 |
| AS202412 | Omegatech LTD | 26 | 4 |
| AS200651 | FlokiNET ehf | 13 | 3 |
| AS51167 | Contabo GmbH | 13 | 1 |
Hiding the Operation Behind Cloudflare
Of the 246 IPv4 addresses identified, 168 belong to Cloudflare AS13335, representing 68% of the total.
Each domain that the attacker places behind the proxy is assigned a pair of IP addresses at Cloudflare’s edge, typically within the 104.21.X.X and 172.67.X.X segments. Out of the 168 IPs, 166 resolve to a single domain; therefore, there are no shared addresses that would allow pivoting to the rest of the operation via passive DNS. However, the proxy does not always successfully hide the backend infrastructure: for 36 of the domains created behind the proxy, passive DNS ended up exposing the real IP, while only 23 registered no exposure (although several of the latter were observed active during the campaign).
This dynamic is clearly reflected when filtering the constellation by this AS: domains are observed orbiting the core without apparent connection, coexisting with domains at the center of activity assigned to both Cloudflare IP addresses and dedicated IPs controlled by the attacker—the latter being the reason it was possible to reconstruct the cluster. Additionally, the satellite domains are domains currently undergoing a “warming-up” process for future use
Impersonated Brands
Financial
In this branch of the attack flow, two fraudulent sites are generated in sequence: first, the replica of the utility company’s payment portal, where the victim believes they are paying their bill; subsequently, upon reaching the authentication phase with the selected financial institution, a second domain replicates the login screen of that bank. This section analyzes this second replica.
The fifteen banking entities that the threat actor chose to impersonate are declared within the captured and deobfuscated source code. Traditional banks coexist with daily-use digital wallets. Each entity has a dedicated configuration that includes its name, color palette, and stylesheet (CSS); therefore, this is not a generic form where only the logo is replaced, but a custom development tailored brand by brand.
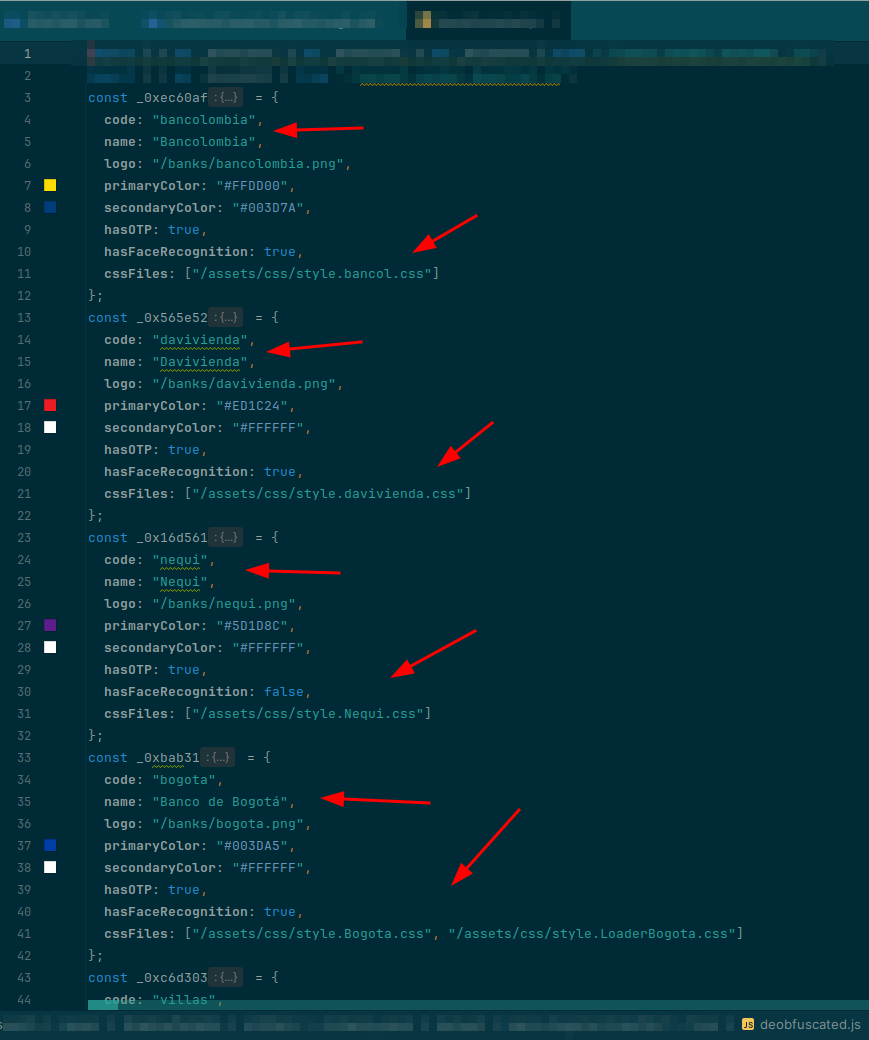
Each entry also specifies the inputs required from the victim for that specific entity, using the parameters hasOTP to request the security token and hasFaceRecognition for live facial biometric capture.
These findings confirm that the threat actor’s capabilities have expanded beyond credential harvesting to include the collection of sensitive biometric data. This information increases the risk profile of the victims, as it can be exploited or traded in other attack vectors.
The panel interface includes additional modules designed to extract further information, including full credit or debit card details. The analysis of the deobfuscated code identified eleven instructions or commands that the attacker’s infrastructure can transmit to the client.
Billers and Payment Gateways
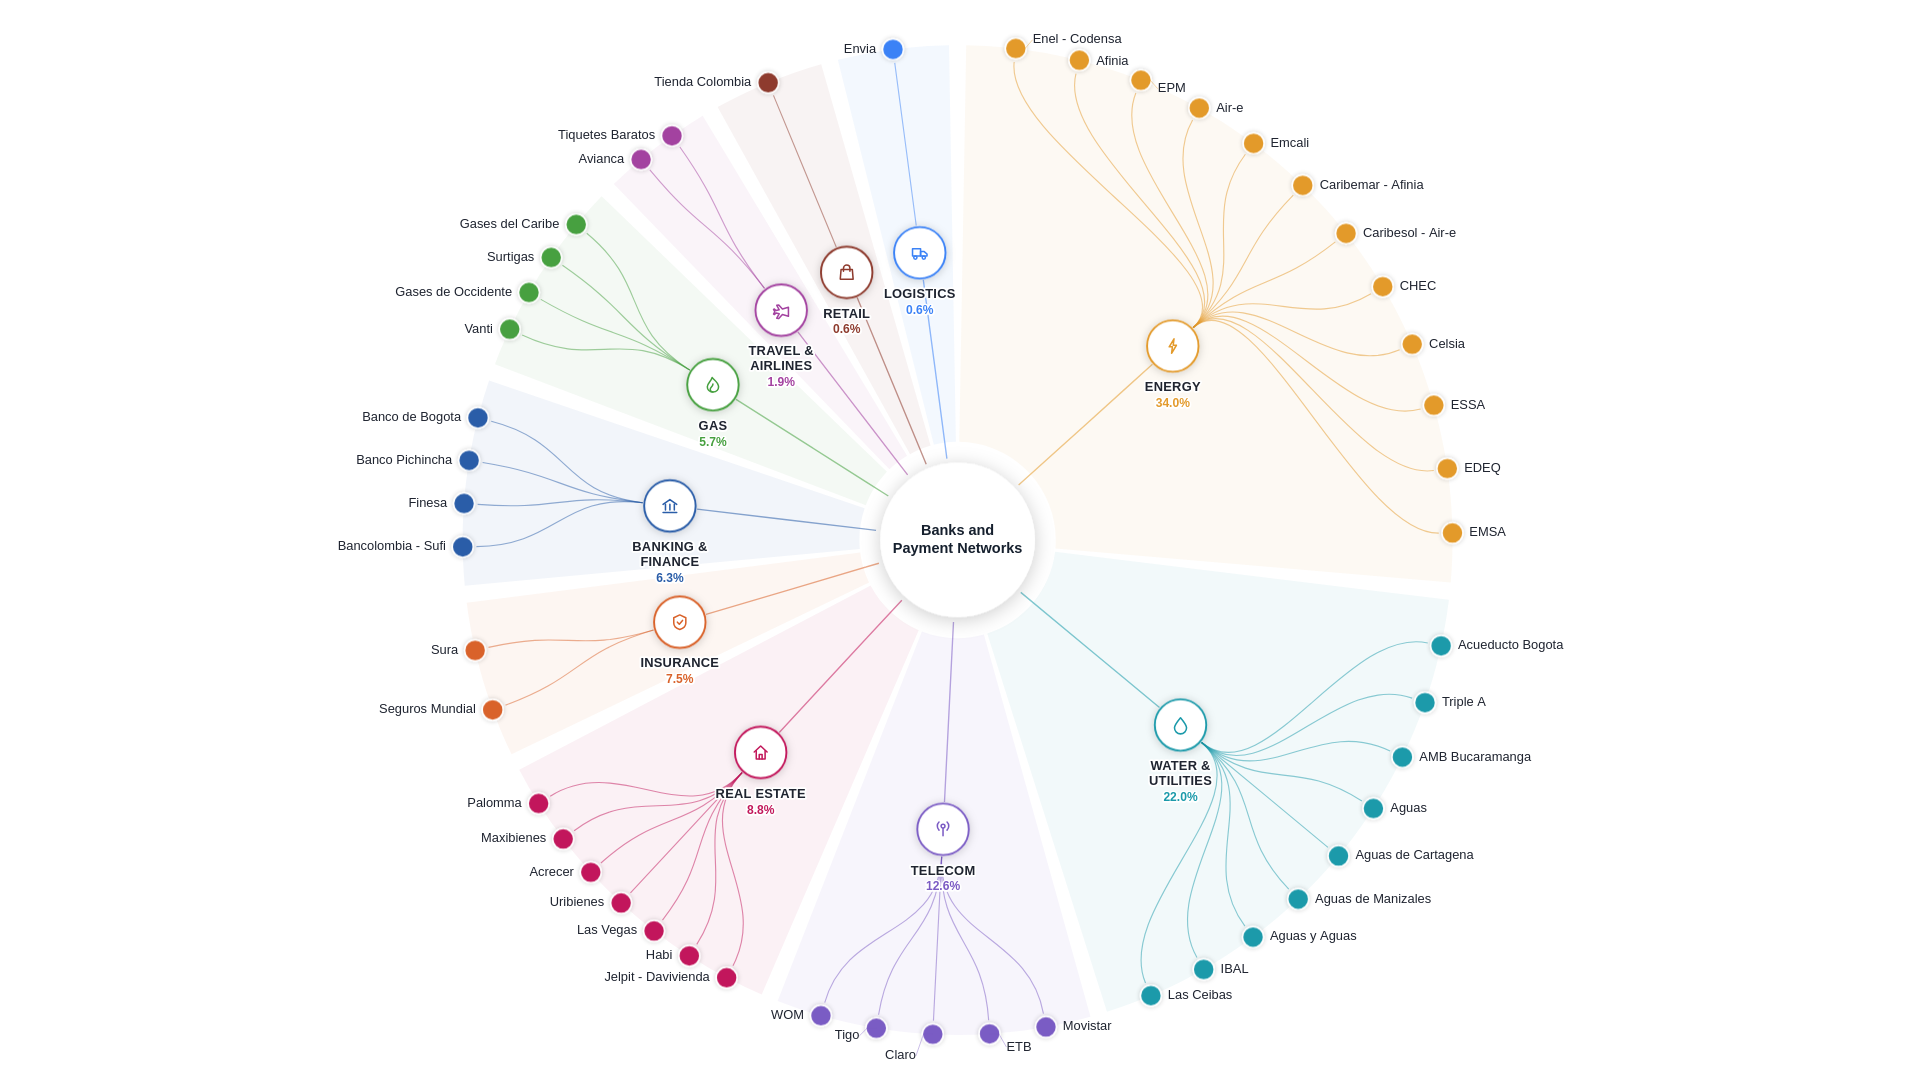
Among the 288 domains identified in the investigation, at least 47 impersonated brands are evident, typically through full replicas of their billing portals hosted on these domains. Along with these brands, 7 payment gateways were identified—some impersonated only in their visual identity and others in the entire payment flow—representing the monetization mechanism of the campaign. These entities belong to 10 different industrial sectors, detailed below:
An Undocumented Threat Actor
Possibly due to its regional scope, no threat intelligence reports attributing or profiling this actor were found. However, the cybercriminal actions identified and detailed in this analysis exhibit an operational volume and technical sophistication that pose a direct threat to our clients and any user of the compromised platforms, with the potential to expand into other neighboring economies.
Based on the indicators of compromise (IoCs) and TTPs consolidated during the investigation, we decided to profile this threat actor and assign them a tracking name. They have been named ShadowParasite, reflecting their operating model: they leverage the reputation of Colombia’s most renowned utility and service brands to deploy a complex, fraudulent payment network designed to harvest sensitive data from victims.
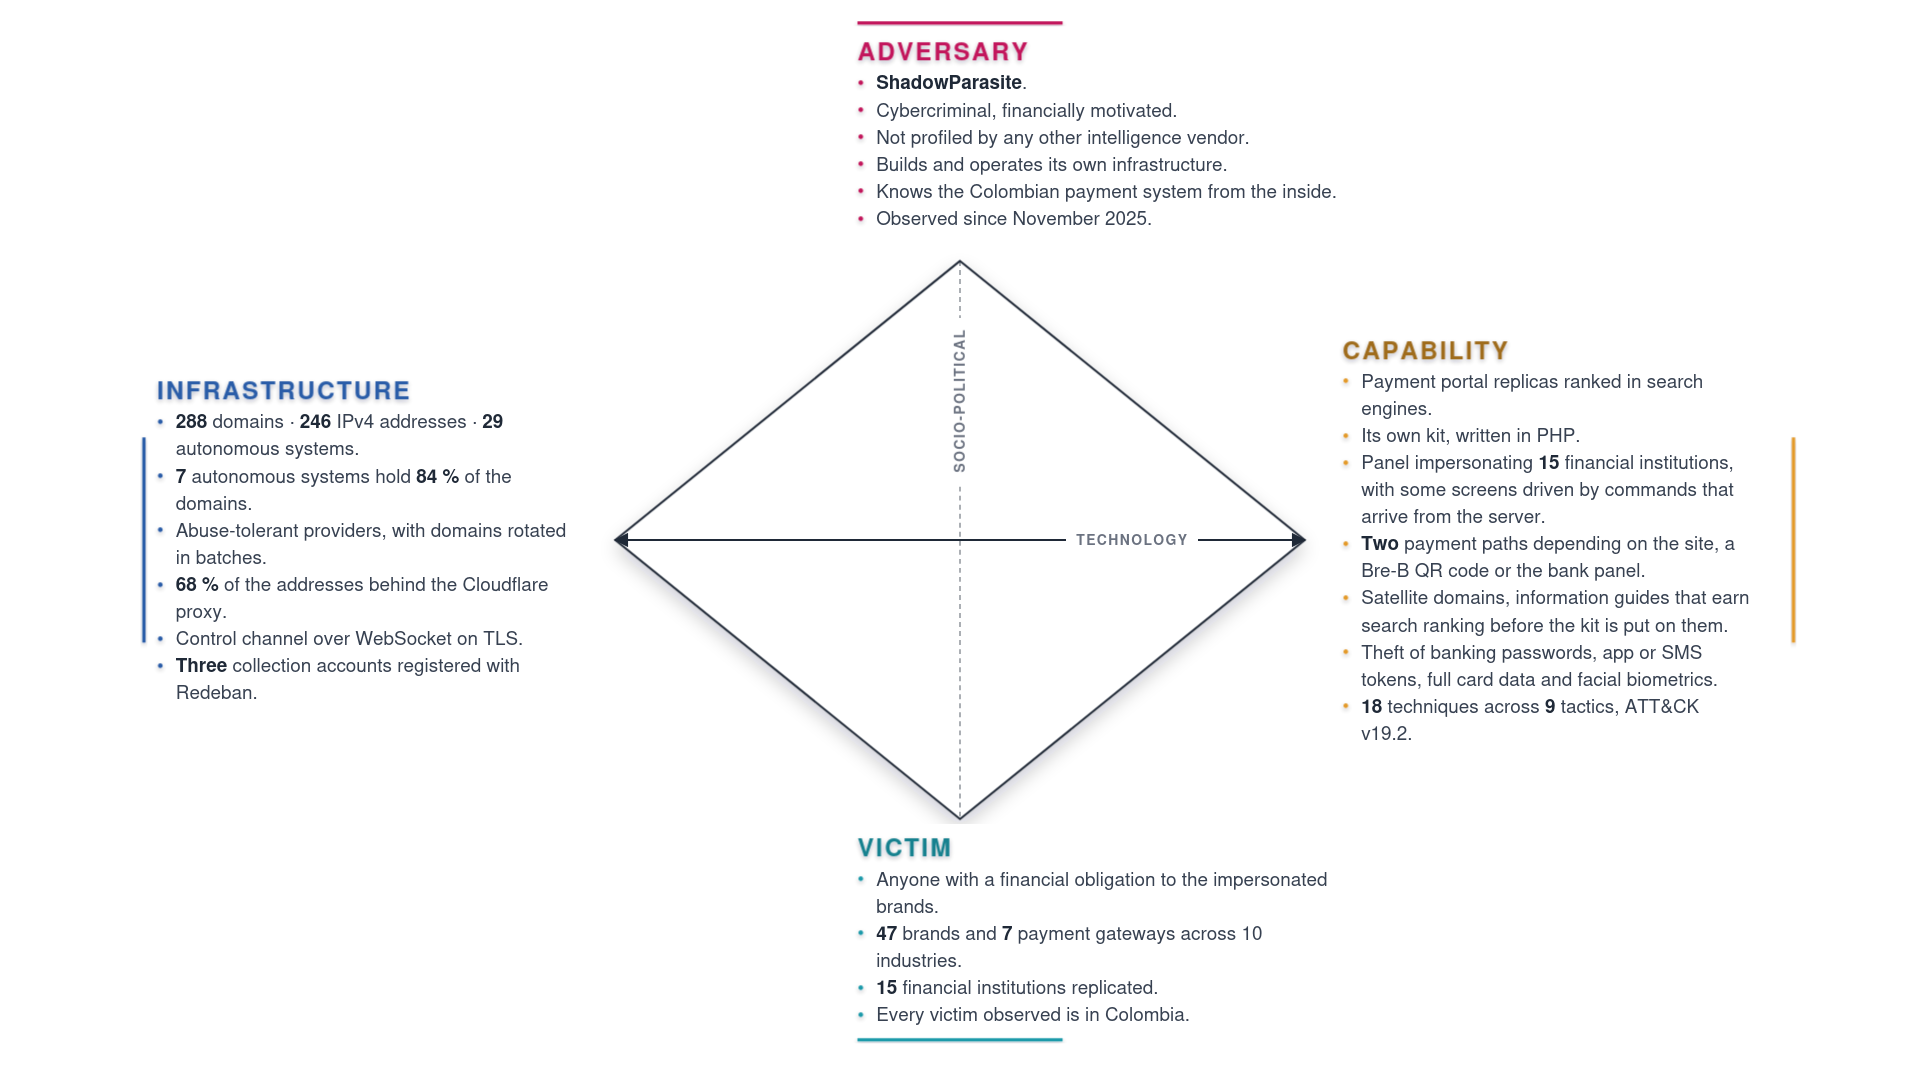
Diamond Model
MITRE ATT&CK
18 techniques across 9 tactics. Enterprise Matrix, ATT&CK v19.2.
| Tactic | ID | Technique | Sub-technique |
| Resource Development | T1583.001 | Acquire Infrastructure | Domains |
| Resource Development | T1583.003 | Acquire Infrastructure | Virtual Private Server |
| Resource Development | T1585 | Establish Accounts | — |
| Resource Development | T1588.004 | Obtain Capabilities | Digital Certificates |
| Resource Development | T1608.005 | Stage Capabilities | Link Target |
| Resource Development | T1608.006 | Stage Capabilities | SEO Poisoning |
| Initial Access | T1566 | Phishing | — |
| Execution | T1204.001 | User Execution | Malicious Link |
| Stealth | T1027 | Obfuscated Files or Information | — |
| Stealth | T1480 | Execution Guardrails | — |
| Stealth | T1684.001 | Social Engineering | Impersonation |
| Credential Access | T1056.003 | Input Capture | Web Portal Capture |
| Credential Access | T1111 | Multi-Factor Authentication Interception | — |
| Discovery | T1082 | System Information Discovery | — |
| Collection | T1125 | Video Capture | — |
| Command and Control | T1071.001 | Application Layer Protocol | Web Protocols |
| Command and Control | T1665 | Hide Infrastructure | — |
| Impact | T1657 | Financial Theft | — |
IoCs
Domains
288 domains.
# Domains identified in this investigation, 237.
- achpse[.]com[.]co
- acrecer-pagos[.]st
- apiscrap999[.]cc
- clientes-acueducto[.]com[.]co
- habi-pagar[.]st
- jelpits-pagos-pse[.]st
- pagar-chec[.]st
- pagar-etb[.]st
- palomma-pagos[.]st
- pse-achcolombia[.]co
- pse-breb[.]st
- uribienes-pago[.]st
- wompagoexpress[.]st
- 999apiscrap[.]cc
- aacueducto[.]com[.]co
- ach-colombia-pagos[.]fun
- achcolombiapagos[.]net
- acueducto-bogota[.]co
- acueducto-bogota[.]st
- acueducto-co-com[.]st
- acueducto-co[.]st
- acueducto-com-co[.]st
- acueducto-de-bogota[.]co
- acueducto-pago[.]st
- acueducto-pagos[.]st
- acueducto-pse[.]st
- acueducto[.]st
- acueductobgta[.]st
- acueductodebogta[.]st
- afinia[.]st
- aire-pagar[.]st
- aire-pagos[.]st
- airepago[.]st
- arrendamientos-las-vegas[.]st
- authcommbank[.]live
- aviancol-tickets[.]st
- avonus[.]cc
- basicinmed[.]cc
- beneficiosy[.]cc
- bienco-pse[.]st
- bogota-acueducto[.]com[.]co
- boton-enel[.]co
- celsiapagos[.]st
- checkin-aviancol[.]st
- claro-pagosrecaudos[.]st
- colombia-pagosenlinea[.]st
- desembolsos-colombia[.]st
- dsct-mov[.]com
- eaabpagos[.]net
- efecty-colombia[.]st
- emcalifacturass[.]com
- emsa-pse[.]st
- enel[.]st
- enelpagos[.]co
- epay[.]dsct-mov[.]com
- epayco[.]beneficiosy[.]cc
- epayco[.]plantelefonia[.]cc
- epayco[.]segmundial[.]cc
- epaycomovistarpagos[.]st
- epaydcto50colombiasas[.]xyz
- epaymovisttarecaud0s[.]st
- epaypagosmovisttarcol[.]st
- epayrecaudosmovistt[.]st
- epayycolombia[.]click
- epm-transaction[.]cc
- epmfacturacion[.]com
- epmfacturas[.]st
- etb-colombia[.]co
- express-unet[.]cc
- facturepago[.]st
- generador-pagos[.]co
- grupo-vanti[.]co
- internal[.]acueducto-co-com[.]st
- jelpit[.]st
- jelpits[.]st
- mail[.]acueducto-co-com[.]st
- mail[.]afinia[.]st
- maxibienes-pagos[.]st
- mediumscrap[.]cc
- movilesepayyjunio[.]sbs
- movistarecaudosepayc0[.]st
- movlstarepaypagos[.]st
- movpays[.]cc
- movt4r-colombia[.]cc
- nooncespro[.]cc
- nq-sas-pagos[.]cc
- onlybot999main[.]com
- onlybot999numbers[.]com
- onlynumbers999[.]cc
- pagar-acueducto-com[.]st
- pagar-enel[.]st
- pagaracueductobogota[.]st
- pagarairecaribe[.]st
- pagarcelsia[.]st
- pagarchec[.]st
- pagaredeq[.]st
- pagarencalifactura[.]st
- pagarfacturatriplea[.]st
- pagarvanti[.]st
- pagatufactura[.]st
- pago-amb[.]st
- pago-enel[.]st
- pago-gascaribe[.]st
- pagoafinifacturas[.]st
- pagoaire[.]st
- pagos-aaa[.]st
- pagos-emcali[.]co
- pagos-etb[.]st
- pagos-gasvanti[.]st
- pagos-gdo-gasesdeoccidente[.]st
- pagos-jelpit[.]st
- pagosachcolombia[.]net
- pagosaguamanizales[.]st
- pagosenel[.]st
- pagosenlinea[.]st
- pagosfinesa[.]st
- pagosonlinemovlstarco[.]st
- pagosportalmoviles[.]st
- pagosrecaudosmovil[.]st
- pay[.]secure-checkout[.]st
- paysimpler-appusaepay[.]com
- pichinchamiles[.]st
- plantelefonia[.]cc
- polizasuramericana[.]org
- portada-inmobiliaria-pagos[.]st
- portal-recaudosurtigas[.]st
- portalrecaudos-gdo[.]st
- portalrecaudosmoviles[.]sbs
- pse-colombia[.]st
- pse-pagos[.]net
- pse-vanti[.]co
- pseachcolombia[.]com
- rastreo-envia-colombia[.]st
- recauddmovistcol[.]xyz
- recaudodigitalmov[.]st
- recaudomov[.]st
- recaudomovistarcolombia[.]st
- recaudoscolombia[.]st
- recaudosmovtt[.]xyz
- recaudosmovttt[.]xyz
- schoolplain[.]cc
- secure-checkout[.]st
- segmundial[.]cc
- service-empresa[.]st
- supersnasvrlt-appcolcb2[.]st
- surtigas[.]st
- tiquetesbaratos[.]st
- tools999[.]cc
- tools999[.]co
- tuespacioinmobiliario-pagos[.]st
- unet-express[.]cc
- 048003hqhola[.]mitelefon[.]cc
- aceptar-pagos-breb[.]fedcol[.]cc
- achseguros[.]com
- activa[.]mitelefon[.]cc
- acueducto[.]cc
- aguadelhogar[.]com
- aguayalcantarillado[.]cc
- aldia[.]mitelefon[.]cc
- app[.]mitelefon[.]cc
- b2cepmco-b2clogin[.]site
- bre-b-desembolso[.]site
- cancel[.]mitelefon[.]cc
- cancelar[.]segmundial[.]cc
- cardplus-bogota[.]cc
- celtelep[.]in
- dato[.]beneficiosy[.]cc
- datos[.]celtelep[.]in
- datos[.]mitelefon[.]cc
- dia[.]segmundial[.]cc
- enlinea-colombia[.]com
- epay-newcol[.]cc
- epay[.]mitelefon[.]cc
- epay[.]telefonia[.]cc
- epayco[.]mitelefon[.]cc
- express-facturas[.]cc
- factmovil[.]mitelefon[.]cc
- factura[.]mitelefon[.]cc
- factusmovil[.]cc
- falasolic-plus2[.]st
- falasolic-plus3[.]st
- fedcol[.]cc
- fija[.]beneficiosy[.]cc
- fija[.]mitelefon[.]cc
- fija[.]telefonia[.]cc
- flybaratoscolombia[.]cc
- flybaratoscolombia[.]lat
- guiadeviajescolombiaturismoymas[.]com
- hogar[.]mitelefon[.]cc
- hola[.]mitelefon[.]cc
- mando-internet[.]cc
- mi-tigo-pago[.]express-facturas[.]cc
- mitelefon[.]cc
- mix[.]mitelefon[.]cc
- moonpro999[.]xyz
- mora[.]mitelefon[.]cc
- mov-co[.]cc
- movis[.]cc
- movistrpay[.]xyz
- msecure-epayco[.]cc
- mt[.]mitelefon[.]cc
- new-checkout-epayco[.]cc
- p0lizacardalf4[.]com[.]co
- pagmovil[.]mitelefon[.]cc
- pagos-comercial[.]online
- pagos[.]acueducto[.]cc
- pagos[.]telefonia[.]cc
- pay[.]segmundial[.]cc
- personas-club[.]cc
- planmvstar[.]mitelefon[.]cc
- portal-central[.]fun
- postpagtelefonia[.]xyz
- preaprobados-colombia[.]cc
- pse[.]telefonia[.]cc
- saldo[.]mitelefon[.]cc
- saldo[.]telefonia[.]cc
- seg[.]segmundial[.]cc
- seguro[.]telefonia[.]cc
- servicios[.]telefonia[.]cc
- sites-essa-placetopay[.]cc
- sites-placetopay[.]co
- sitesessaplacetopay[.]cc
- soat[.]segmundial[.]cc
- soatplacamundial[.]cc
- sportalpay[.]site
- st[.]mitelefon[.]cc
- telefonia[.]cc
- total[.]mitelefon[.]cc
- turismoyvueloscol[.]com
- tuturismoyvuelos[.]co
- vantclubs[.]lat
- virtlalbogota[.]com
- vuelaporcolombiatravel[.]lat
- vuelosyviajesmasbaratos[.]com
- web-conjuntosjelpi[.]co
- westernunion-company[.]cc
- xn--lw9h[.]fm
# Domains identified in the first investigation, 52.
- afiniapagarfactura[.]st
- afiniapagarpse[.]st
- afiniapagos[.]st
- afiniapse[.]st
- aguasb[.]st
- aguasdecartagena[.]st
- aguasyaguaspse[.]st
- airepagos[.]st
- airepse[.]st
- caribemar-facture-co[.]st
- caribesol-facture[.]st
- emcalipagos[.]st
- enelcodensapse[.]st
- epmfactura[.]st
- epmpagarfactura[.]st
- epmpagos[.]st
- epmpse[.]st
- es[.]caribemar-facture-co[.]st
- es[.]caribesol-facture[.]st
- es[.]finesa[.]st
- es[.]pagar-sufi-apps-bancolombia[.]st
- es[.]pagos-acueducto[.]st
- es[.]pagos-emcali[.]st
- es[.]pagos-enel[.]st
- es[.]suranlinea[.]st
- finesa[.]st
- ibalpse[.]st
- pagar-factura-afinia[.]st
- pagar-factura-las-ceibas[.]st
- pagar-sufi-apps-bancolombia[.]st
- pagar-sufi-apps[.]st
- pagarbienco[.]st
- pagarhabi[.]st
- pago-acueducto[.]st
- pagos-acueducto[.]st
- pagos-emcali[.]st
- pagos-enel[.]st
- pagoslasvegas[.]st
- psebre-b[.]com
- psebre-b[.]st
- suranlinea[.]st
- tiendacolornbia[.]com
- uribienespagos[.]st
- web[.]caribemar-facture-co[.]st
- web[.]caribesol-facture[.]st
- web[.]finesa[.]st
- web[.]pagar-sufi-apps-bancolombia[.]st
- web[.]pagos-acueducto[.]st
- web[.]pagos-emcali[.]st
- web[.]pagos-enel[.]st
- web[.]suranlinea[.]st
IPv4
36 IPs. Only IPs hosting the attacker’s infrastructure are valid IoCs; shared hosting addresses were excluded as indicators to prevent unintended impact on third parties.
- 193[.]109[.]193[.]98
- 193[.]143[.]1[.]226
- 192[.]109[.]200[.]115
- 181[.]41[.]201[.]34
- 45[.]153[.]34[.]157
- 45[.]74[.]3[.]130
- 91[.]92[.]241[.]197
- 95[.]133[.]166[.]118
- 95[.]133[.]166[.]172
- 82[.]147[.]84[.]122
- 45[.]74[.]3[.]163
- 158[.]94[.]210[.]15
- 176[.]65[.]132[.]16
- 176[.]65[.]132[.]201
- 192[.]109[.]200[.]66
- 91[.]92[.]47[.]170
- 46[.]151[.]182[.]143
- 176[.]65[.]132[.]146
- 45[.]156[.]87[.]243
- 91[.]92[.]47[.]114
- 192[.]109[.]200[.]236
- 85[.]11[.]167[.]136
- 88[.]80[.]17[.]230
- 91[.]92[.]40[.]221
- 91[.]92[.]47[.]237
- 192[.]109[.]200[.]218
- 84[.]11[.]167[.]131
- 84[.]200[.]80[.]216
- 85[.]11[.]167[.]141
- 91[.]72[.]47[.]171
- 91[.]92[.]40[.]133
- 91[.]92[.]47[.]38
- 91[.]92[.]47[.]51
- 94[.]26[.]106[.]90
- 94[.]26[.]106[.]92
- 95[.]11[.]167[.]131