October, 2026
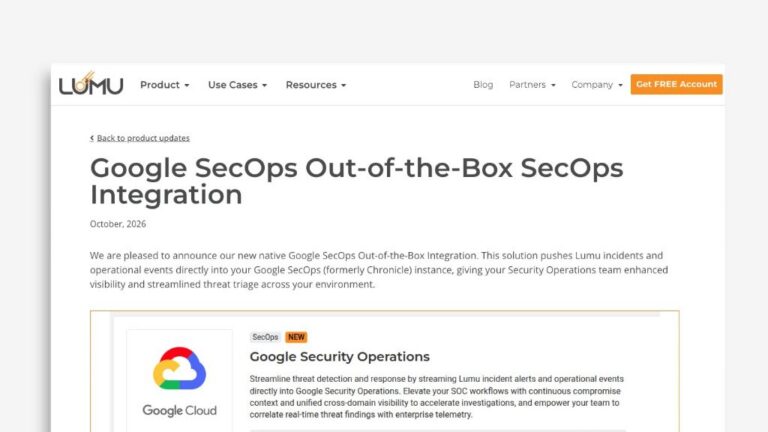
We are pleased to announce our new native Google SecOps Out-of-the-Box Integration. This solution pushes Lumu incidents and operational events directly into your Google SecOps (formerly Chronicle) instance, giving your Security Operations team enhanced visibility and streamlined threat triage across your environment.
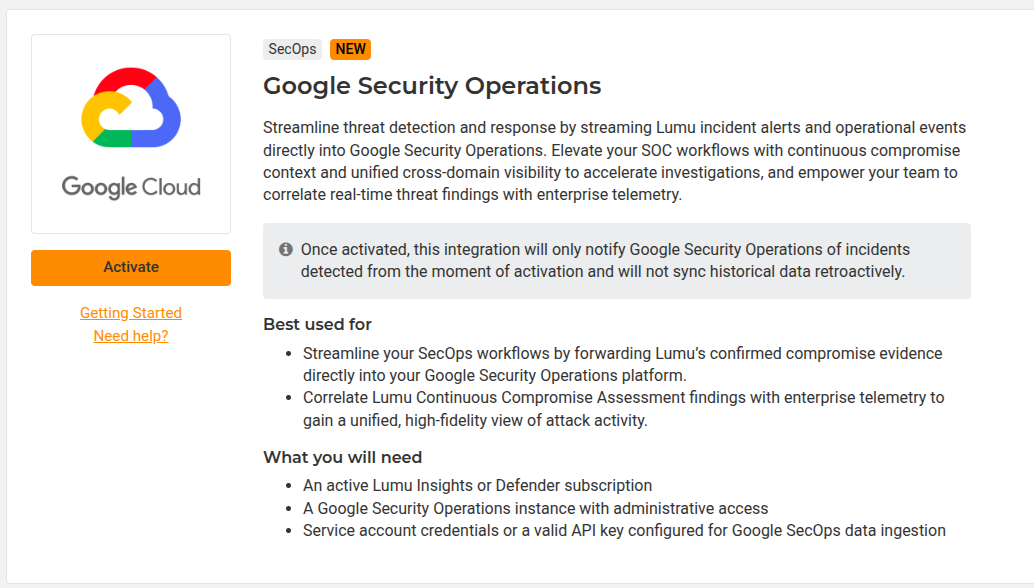
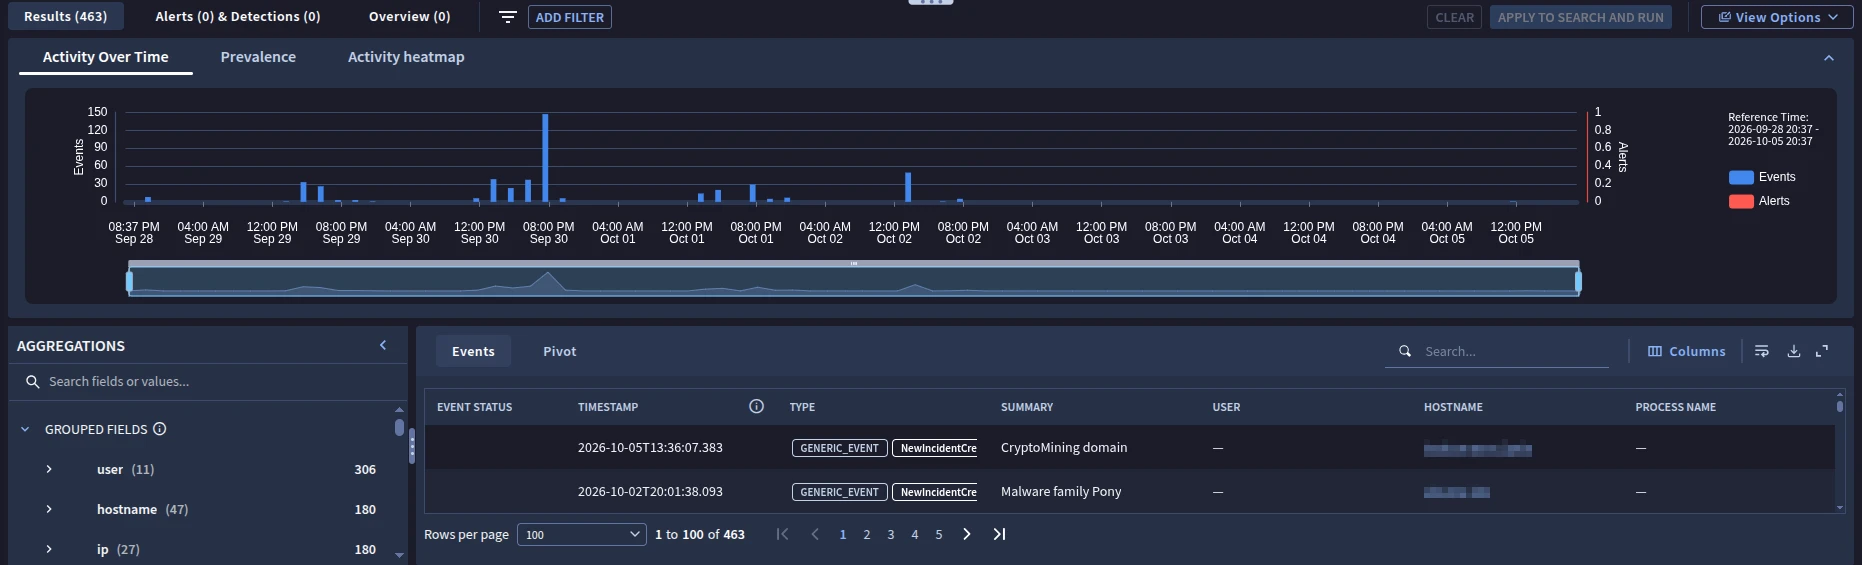
The Google Security Operations Out-of-the-Box Integration is designed to deliver unified event management and effortless telemetry flow:
- Unified SOC Visibility: Centralize compromise context by streaming Lumu real-time evidence alongside enterprise telemetry into a single platform, streamlining security operations for teams of all sizes.
- Accelerated Threat Mitigation: Empower security analysts with real-time compromise context to make faster, wiser remediation decisions and strengthen overall ecosystem cyber resilience.
- Streamlined Search & Retrospective Threat Hunting: Instantly query, correlate, and analyze collected Lumu threat telemetry within your Google SecOps console using simple vendor searches (metadata.vendor_name = “Lumu”) or custom YARA-L detection rules.
To activate this integration, log in to the Lumu Portal and navigate to Integrations > Apps. For prerequisite setup details and full configuration steps, please review our technical documentation.