October, 2026
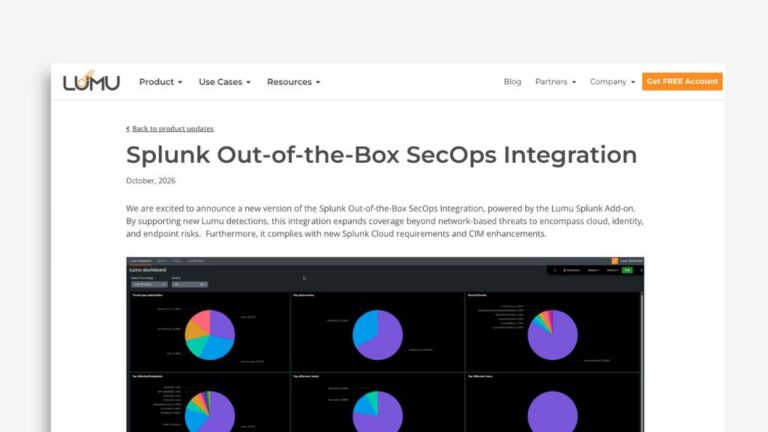
We are excited to announce a new version of the Splunk Out-of-the-Box SecOps Integration, powered by the Lumu Splunk Add-on. By supporting new Lumu detections, this integration expands coverage beyond network-based threats to encompass cloud, identity, and endpoint risks. Furthermore, it complies with new Splunk Cloud requirements and CIM enhancements.
The Lumu Splunk Add-on is designed to deliver unified event management and accelerate threat hunting across your environment:
- Comprehensive Event Sync: Automatically processes both detection-related events and operational status updates or response actions.
- Standardized CIM Mapping: Maps collected events directly to the Splunk Common Information Model (Alerts model for detections and Change model for operational events).
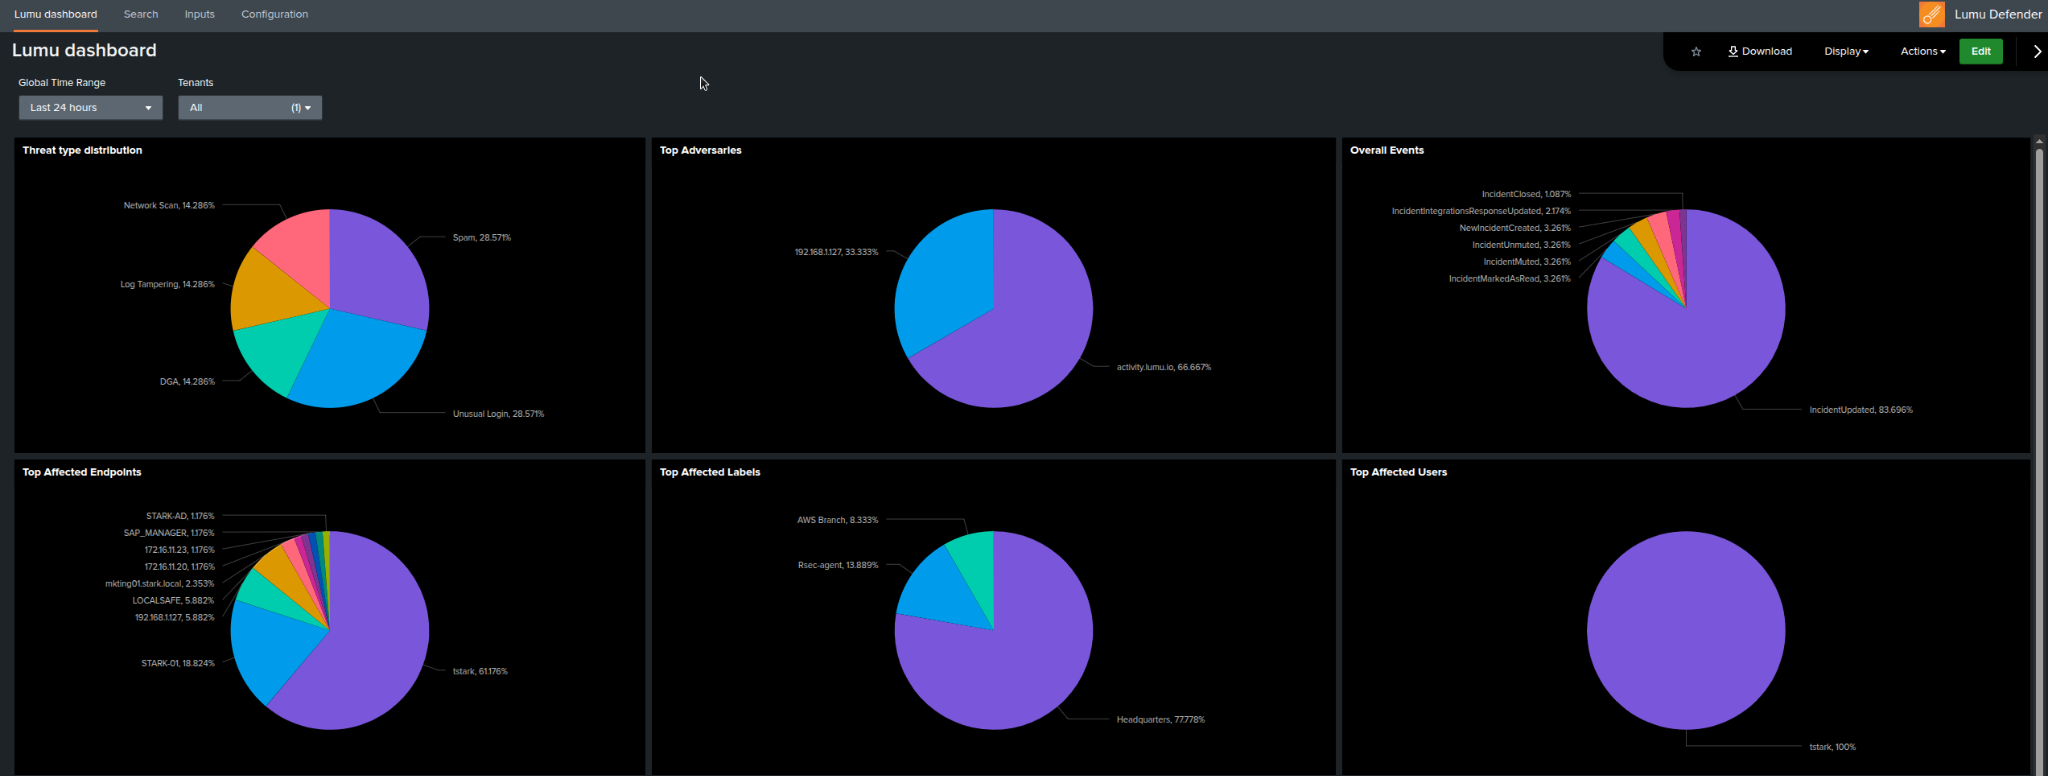
- Dedicated SecOps Dashboard: Offers at-a-glance operational statistics, flexible time-range controls, and tenant-level filtering for multi-source management.
For more information on this integration, please review our technical documentation.